Developer Admin Rights
Remove Admin Rights,
Elevate Dev Tools

Securden seamlessly elevates trusted developer tools like IDEs, compilers, package managers without granting admin rights. Builds keep moving while developers remain standard user.
Enter a proper email address.
Remove Admin Rights
ARROW ELECTRONICS
Kongsberg Defence & Aerospace AS
IMA Financial Group
Credo Semiconductor
Carpenter
Dark Matter Technologies LLC
Setec
Init.de
Communications & Power Industries LLC
Shell Australia
Central Bank of Bahamas
Eppendorf Manufacturing Corporation
University of Western Australia
ARROW ELECTRONICS
Kongsberg Defence & Aerospace AS
IMA Financial Group
Credo Semiconductor
Carpenter
Dark Matter Technologies LLC
Setec
Init.de
Shell Australia
Central Bank of Bahamas
Communications & Power Industries LLC
Eppendorf Manufacturing Corporation
University of Western Australia

Why Granting Admin Rights to Developers Increases Security Risk?

Developers need elevated access more than other teams, so engineering becomes the exception to every security policy.

Standing admin by default

Devs get permanent rights just to avoid workflow interruptions.

High-value targets

A compromised dev machine hands attackers admin-level access.

Malware inherits rights

Anything executing under an admin account runs with full privileges.

No endpoint visibility

Security teams can't see sensitive activities on dev workstations.

Securden Helps Enforce Least privilege, Without Slowing Down Development

Policy-driven privilege elevation for the tools developers actually use.

01 — Seamless development

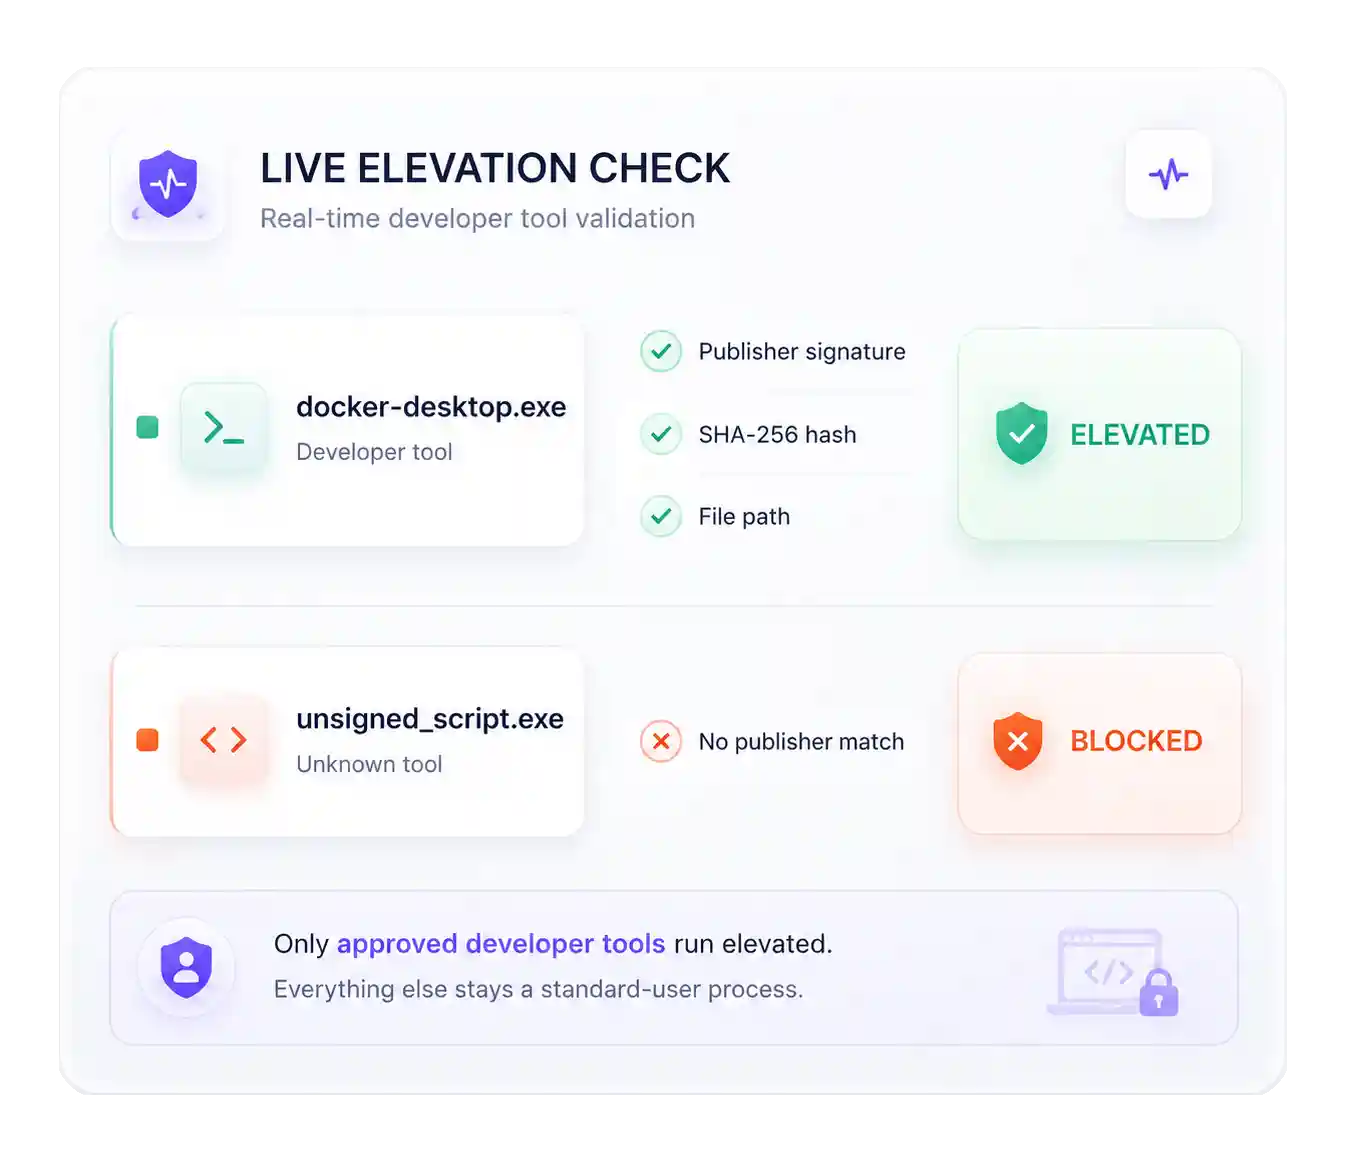
Elevate only approved developer tools

Trusted dev applications run elevated; unnecessary admin access is prevented by default.

02 — Pre-built policies for dev tools

Built for modern dev environments

Policies cover IDEs, compilers, SDK installers, package managers, container platforms, and build tools.

03 — Restrict and control admin rights

Block unauthorized elevation attempts

Only approved tools get admin rights; everything else runs as a standard-user process.

04 — Centralized policy engine

Centrally manage developer policies

Define and manage privilege rules for engineering teams from one console, consistent across every endpoint.

Data-Driven Privilege Governance

Comprehensive Audits

Actionable audits of privileged activity help identify policy gaps and reduce friction in elevating developer applications.

Actionable Insights

Insights on policy gaps help you tweak policies to streamline privilege elevation. Smarter policies help completely automate privilege elevation over the time.

How It Works?

IT Admin sets it up:

  • Remove standing local admin rights from developer workstations.
  • Define trusted applications and dev tools using publisher, signature, hash, filename, or path.
  • Configure policies for seamlessly elevating approved and trusted developer applications.

Developer just builds:

  • Launches IDEs, compilers, or installers normally.
  • Securden automatically elevates only the approved applications.
  • Everything else keeps running without admin rights.
IN THEIR OWN WORDS
Before Securden, we had significant difficulty restricting admin access and managing software installations. After implementing Securden, everything came under control. We can now precisely manage who can install software and what privileges users have on their endpoints.
Arunachalam
Arunachalam Shenkodi IT Team, Aspire Systems
CUSTOMER SUCCESS STORY
How Aspire Systems Took Control of Endpoint Admin Rights with Securden

See how Aspire Systems eliminated local admin rights and gained control over software installations, and administrative access using Securden.

Eliminate Admin Rights

Discovered and eliminated local admin accounts

Application Control

Governance over software installations and execution

Visibility

Gained insights over app execution and local admin access

Efficiency

Streamlined IT operations with policy governed JIT privileges.

Read the full customer story

What changes you can expect in two weeks?

Productivity

No more raising admin access tickets with IT. Trusted dev tools are elevated whenever required.

Security

Zero standing admin rights for developers. Smaller attack surface across engineering endpoints.

Compliance

Zero Trust and least-privilege alignment for engineering. Full audit logs for every privileged action.

Common dev tools that can be elevated

  • Docker Desktop
  • Visual Studio & VS Code
  • Android Studio & JetBrains IDEs
  • SDK installers & build tools
  • Package managers & runtimes
  • Git & container tools
  • Database management tools

Allow Developers to Build Seamlessly Without Granting Standing Admin Rights

Grant application-level elevation. No permanent admin rights and no IT bottlenecks.

Enter a proper email address.
Securden Help Assistant
What's next?
Request a Demo Get a Price Quote

Thanks for sharing your details.
We will be in touch with you shortly

Thanks for sharing your details.
We will be in touch with you shortly