Not every administrator, developer, help desk technician, vendor, or contractor requires continuous access to critical systems and accounts. Yet, permanently granting access to critical systems increases the risk of insider threats, credential misuse, accidental changes, and compliance violations.
Securden Password Vault for Enterprises helps organizations eliminate standing privileges by replacing always-on access with approval-based Just-in-Time (JIT) access. Users can request access to privileged accounts and systems only when needed, receive credentials after approval from authorized personnel, and retain access only for the approved duration.
By combining approval workflows, temporary privilege elevation, and complete audit trails, Securden enables organizations to implement least privilege without disrupting day-to-day operations.
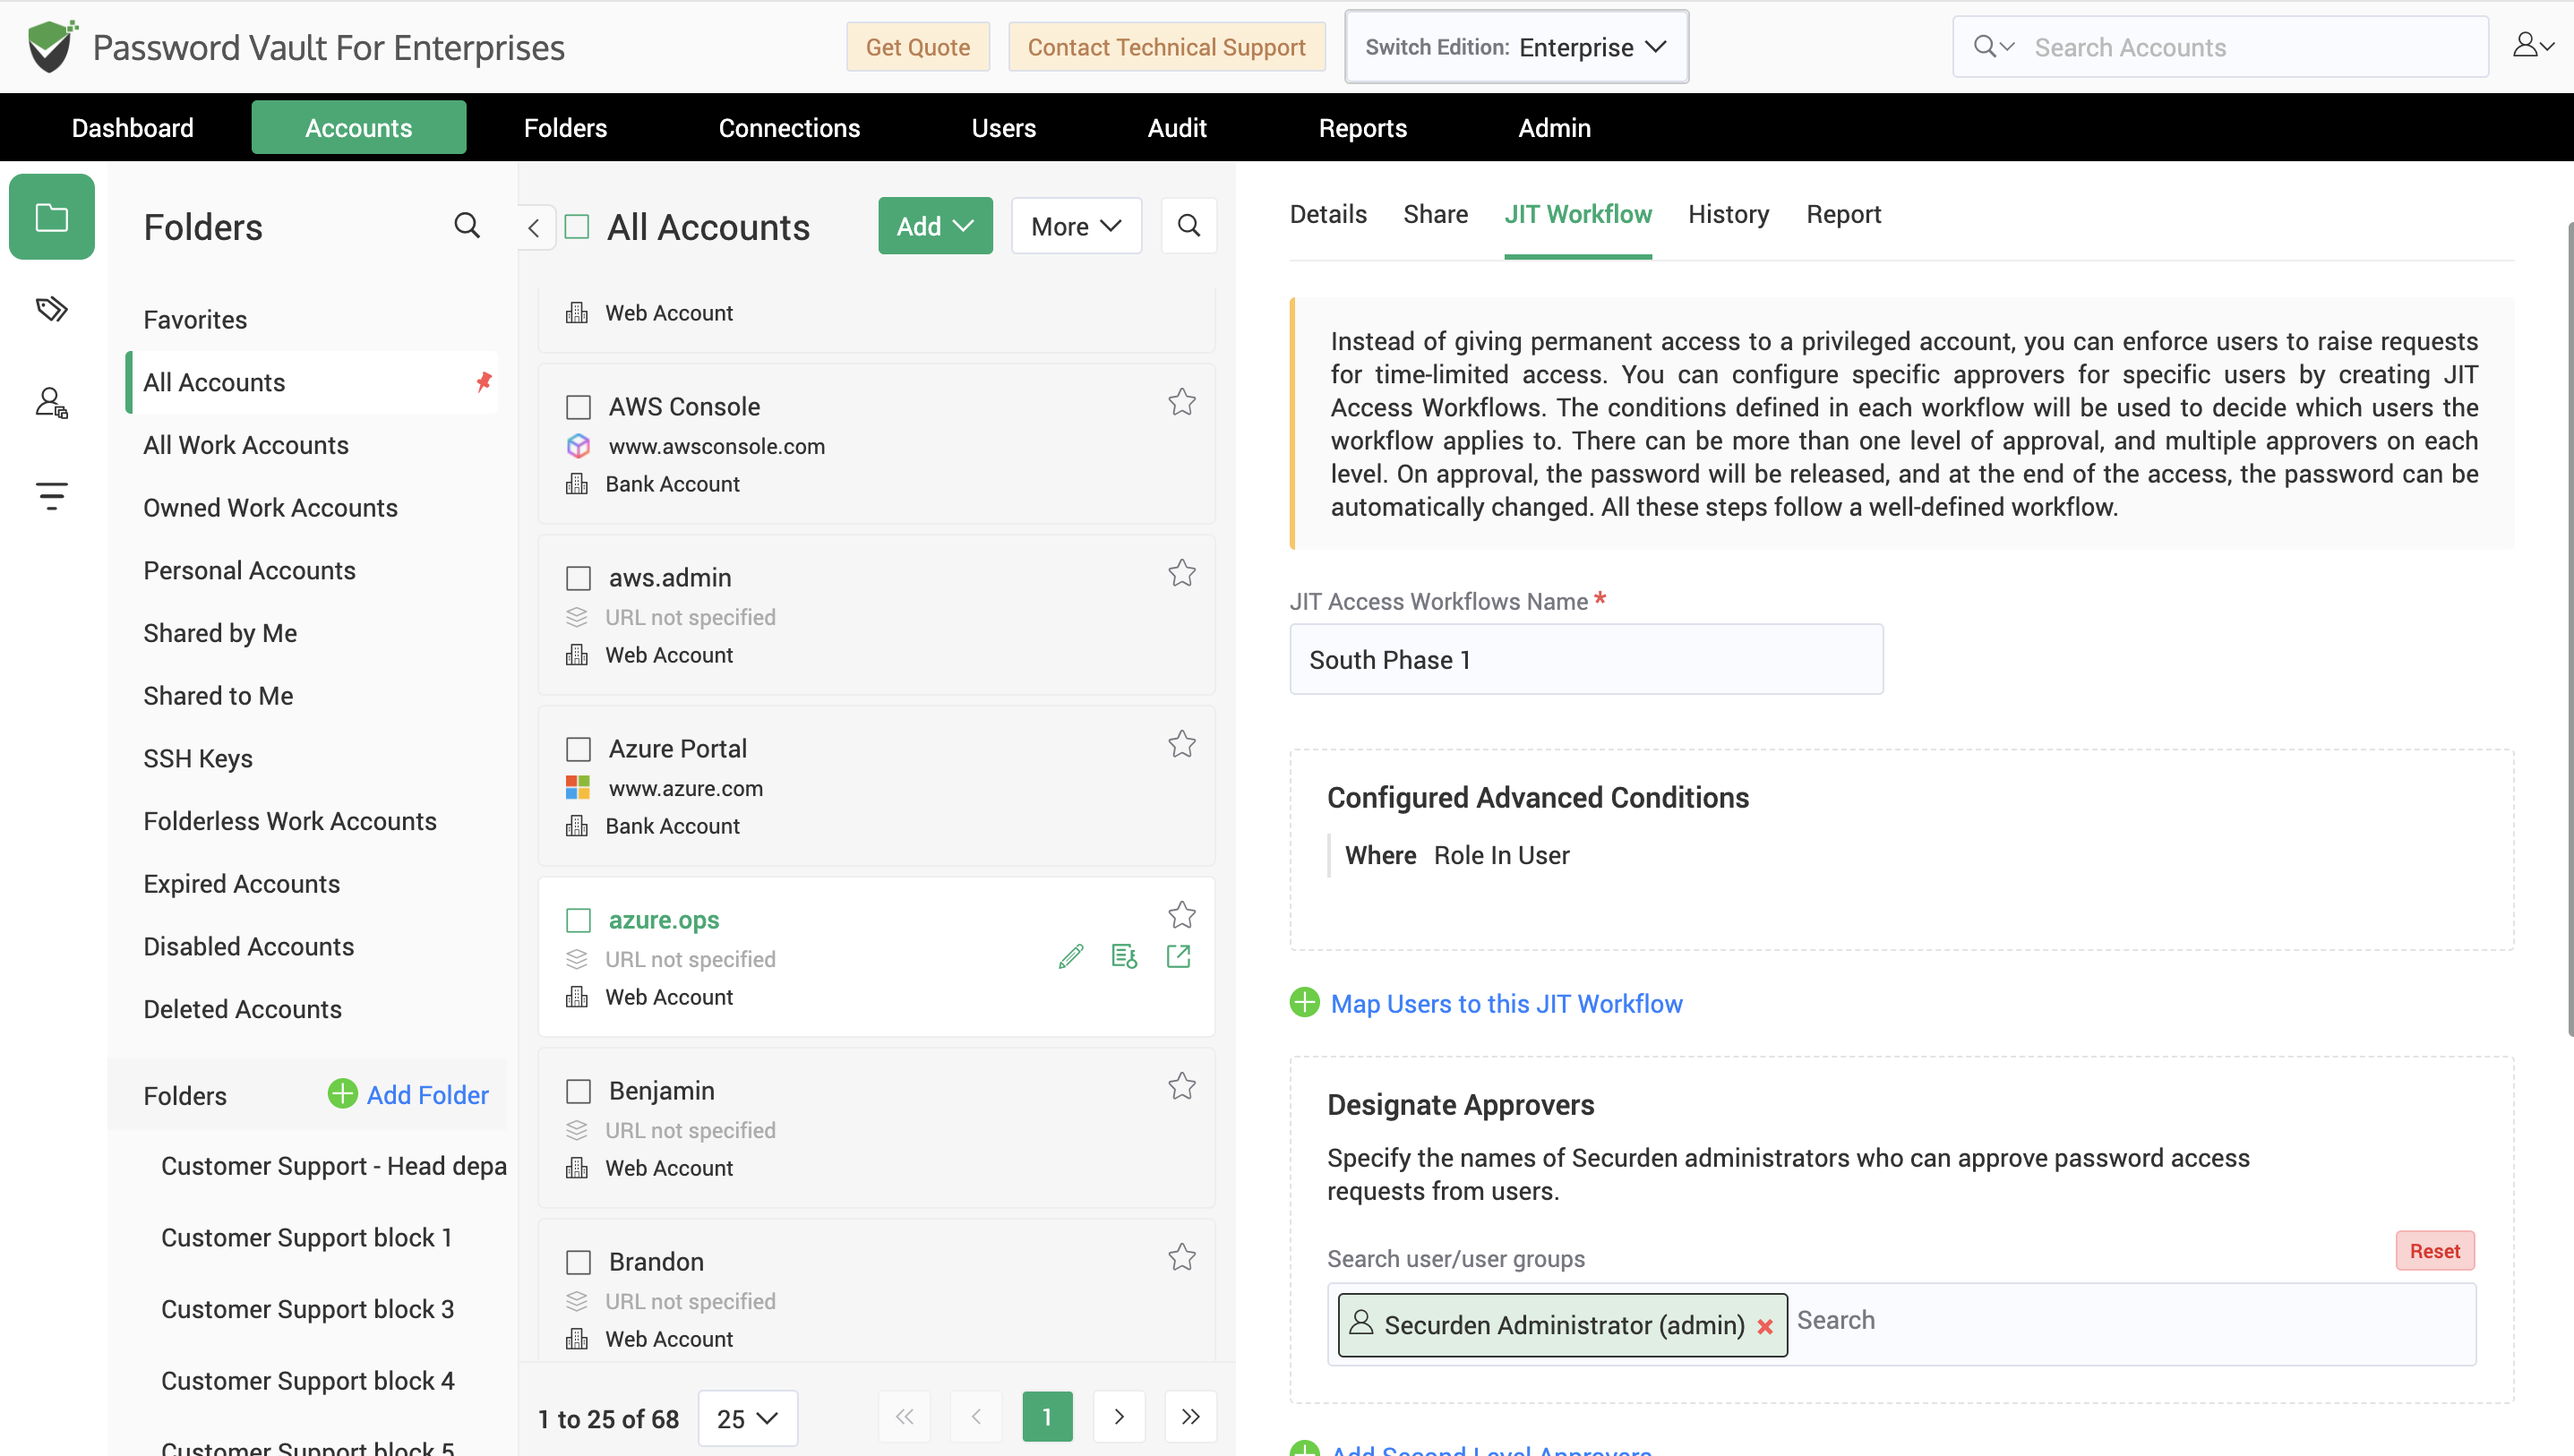
Enforce the Four-Eyes Principle for Sensitive Credentials
Securden Password Vault for Enterprises enables organizations to implement the Four-Eyes Principle by requiring privileged access requests to be reviewed and approved before credentials are released. Every request includes a business justification and is automatically routed to designated approvers based on your organization's approval policies.
This additional layer of authorization ensures that privileged credentials are accessed only for legitimate business purposes while reducing the risk of unauthorized or unnecessary access.
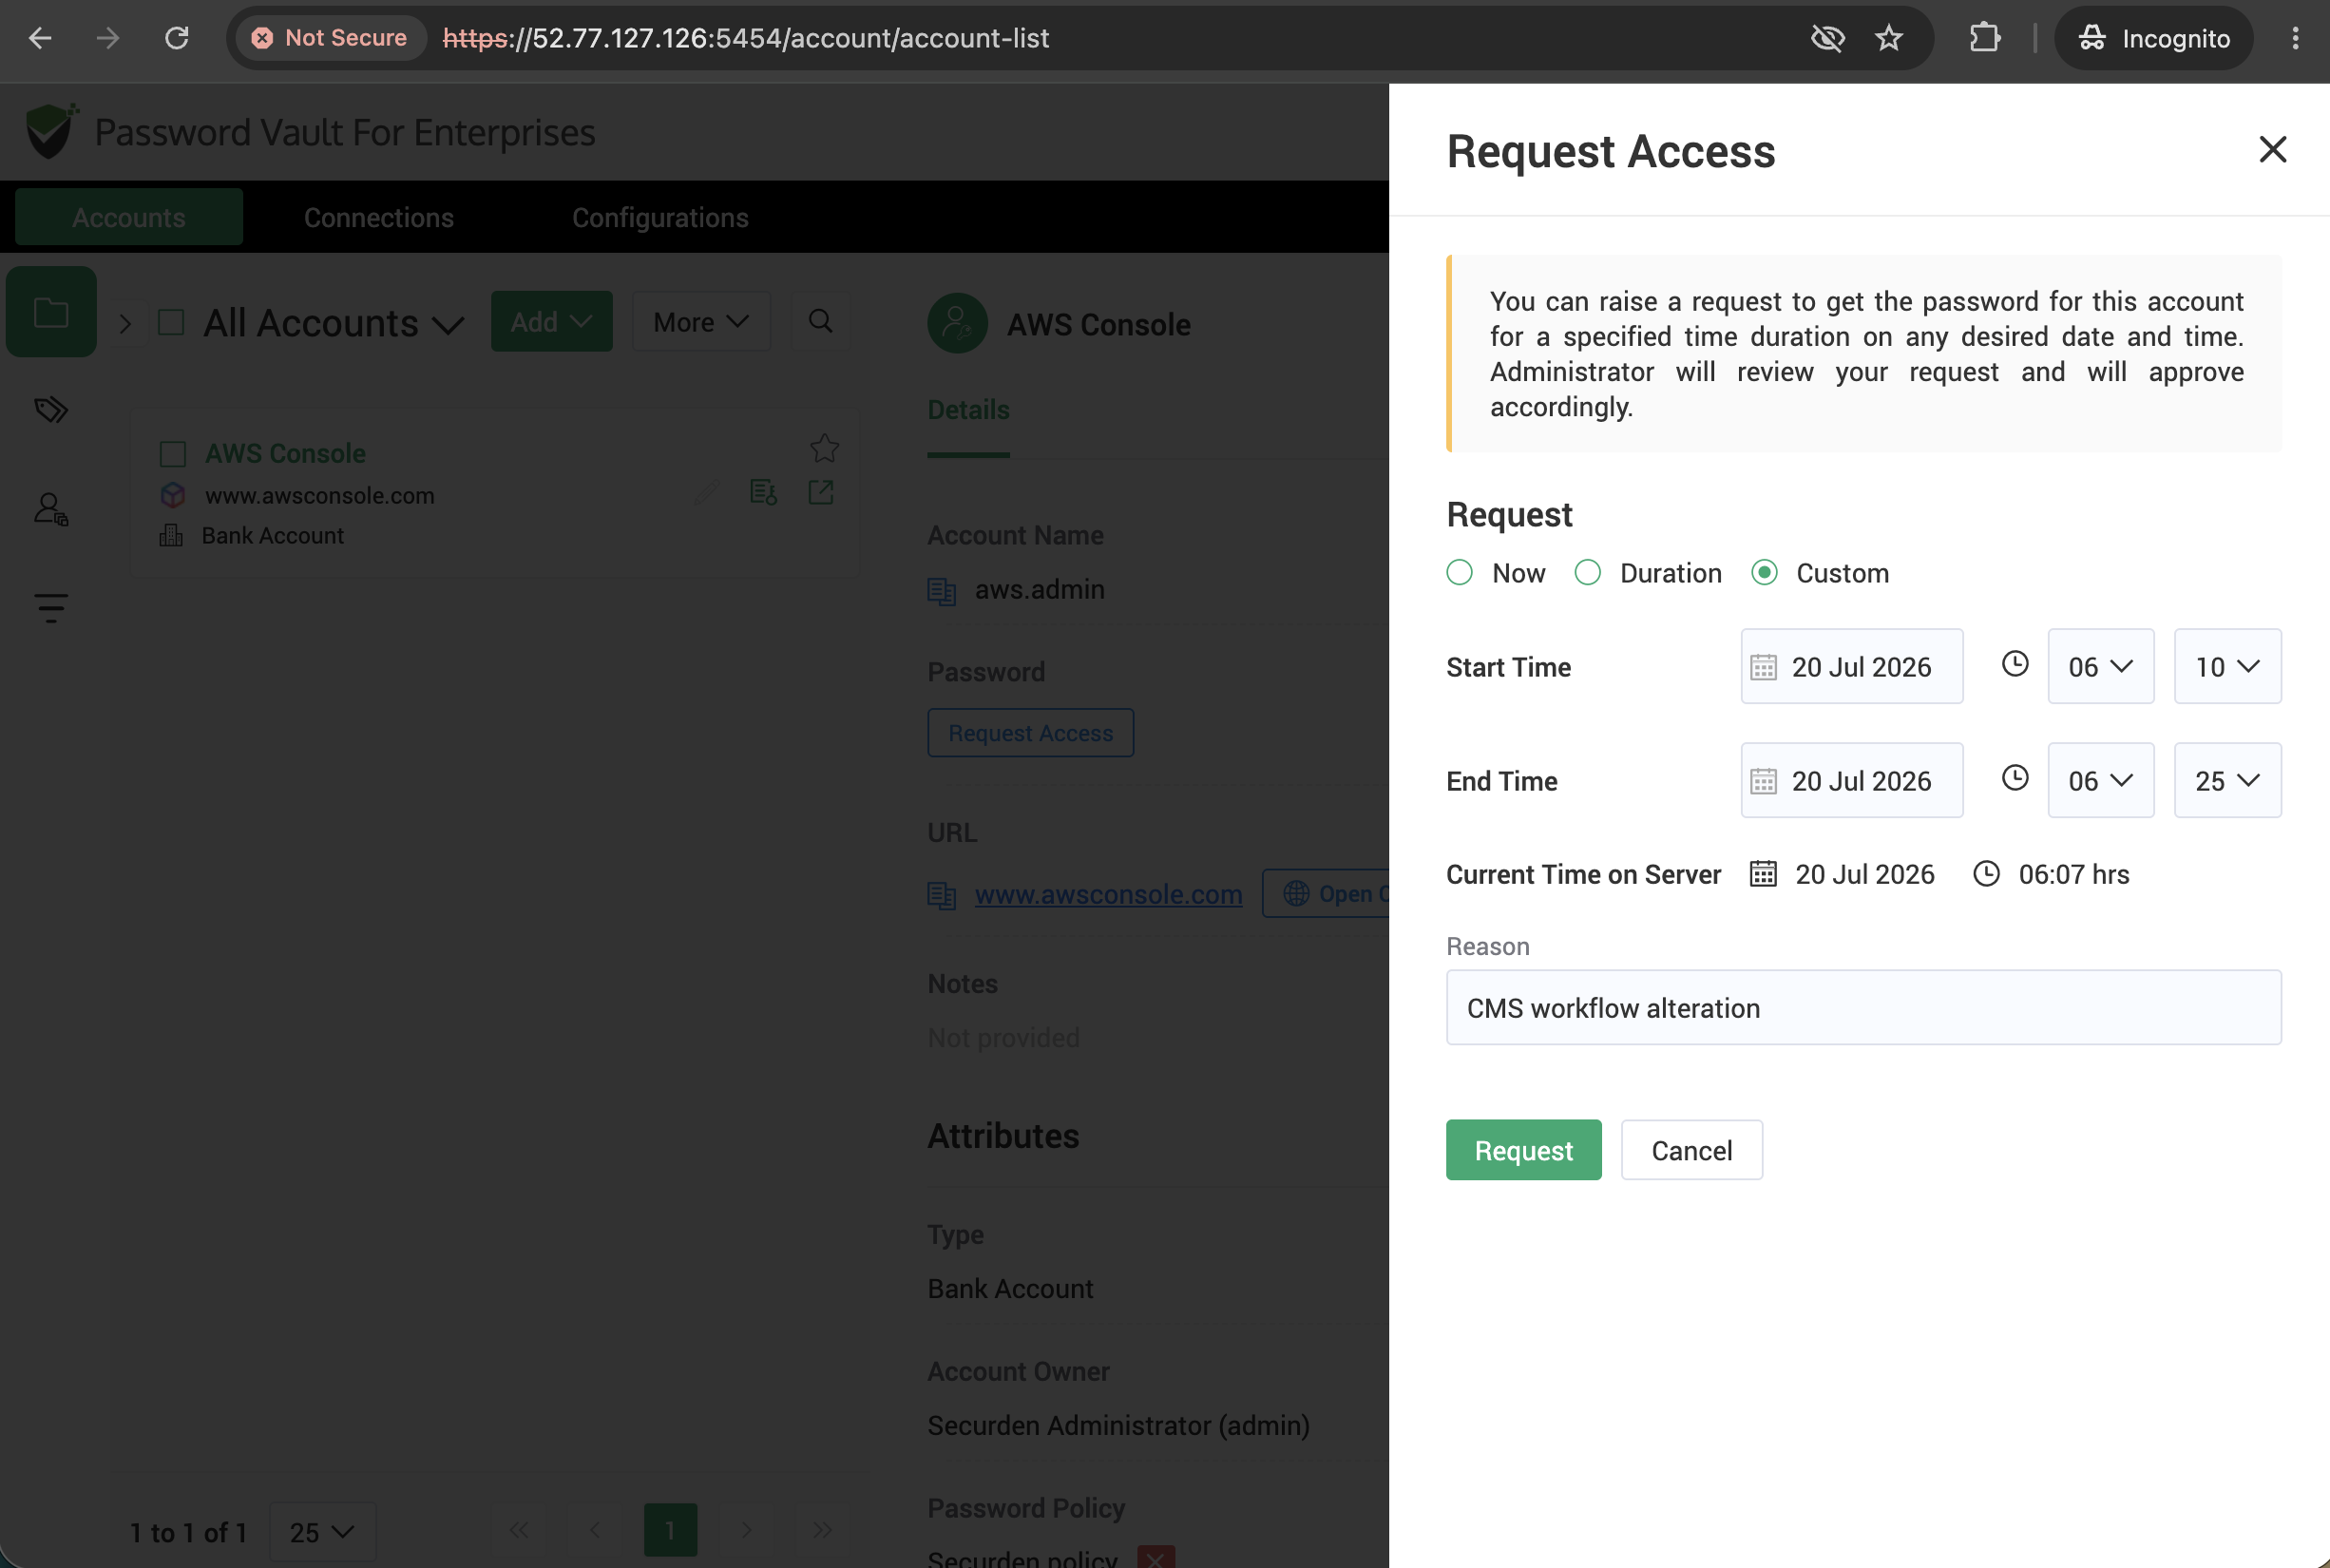
Grant Time-Limited Access Only When It's Needed
Achieve a true Just-in-Time access workflow by granting credentials only for a predefined, approved duration. Once the approved access window expires, access is automatically revoked without requiring manual intervention.
This significantly reduces credential exposure while allowing administrators, developers, vendors, and support teams to complete privileged tasks without unnecessary delays.
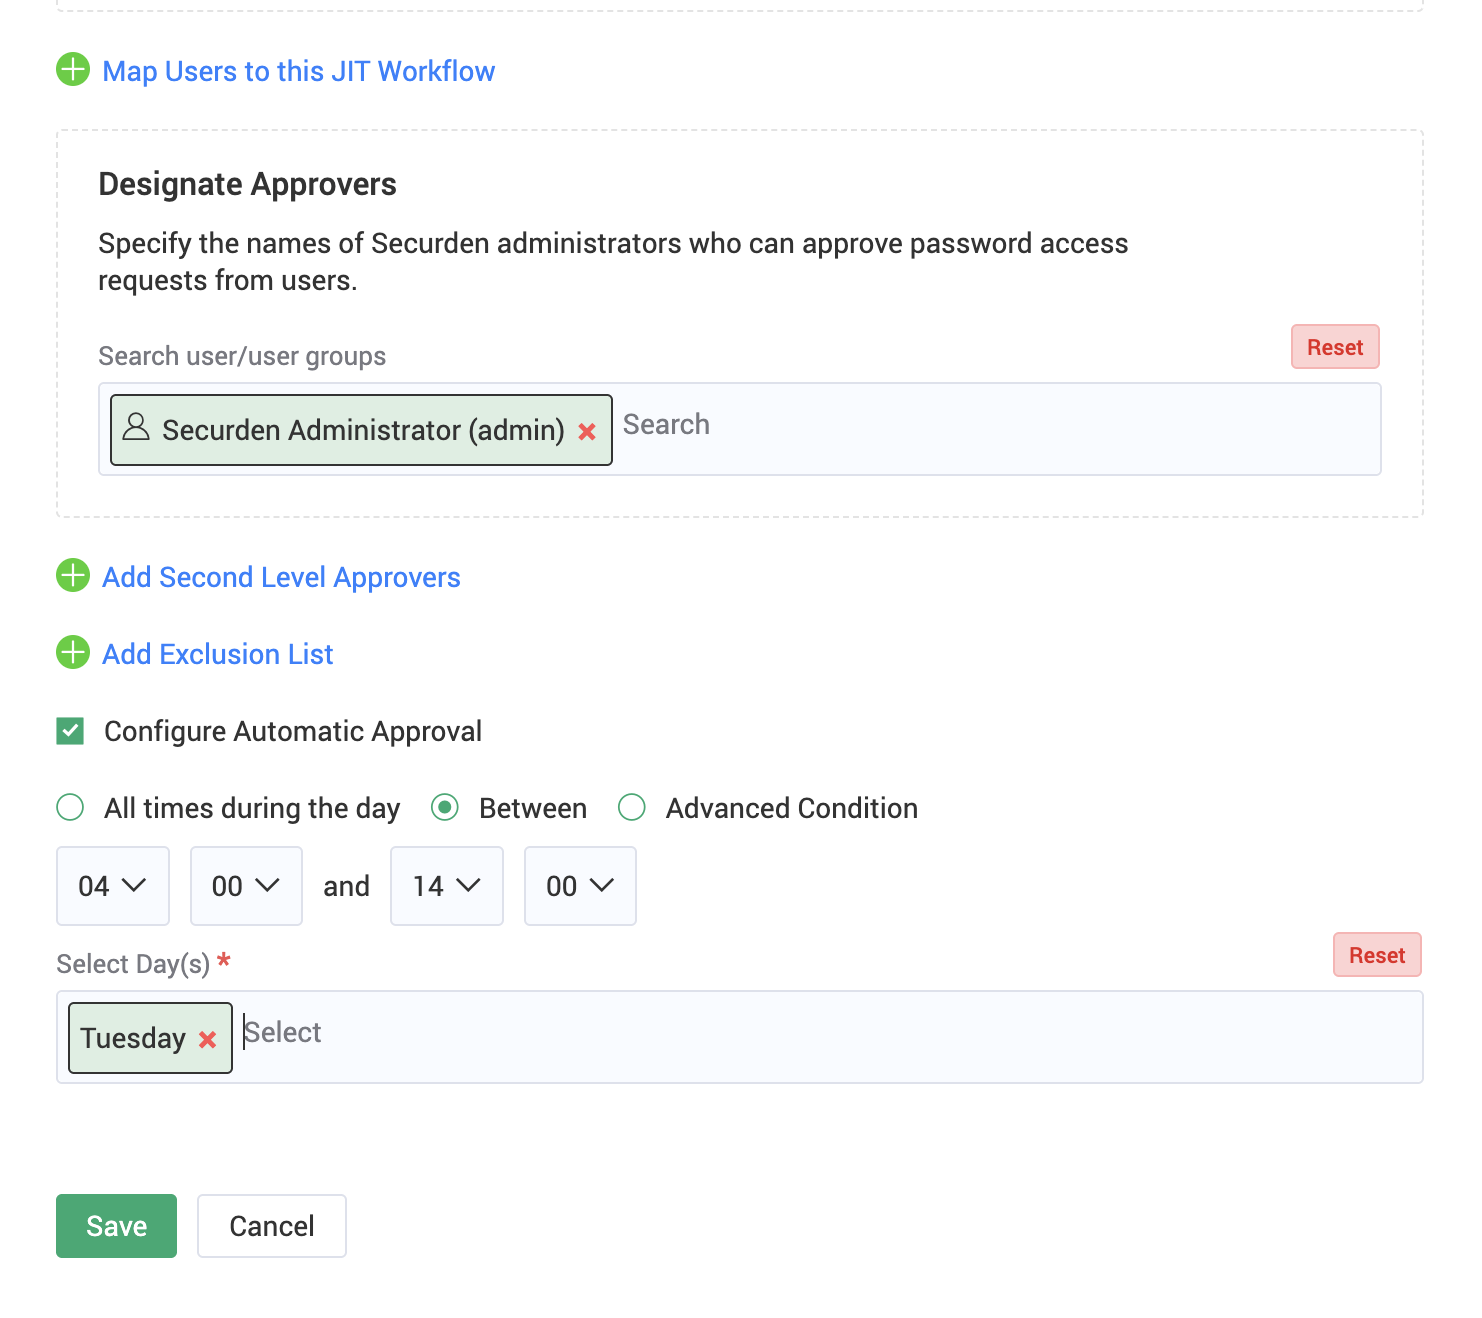
Configure Approval Workflows Around Your Business
Every organization has unique operational and compliance requirements.
Securden Password Vault for Enterprises provides flexible approval workflows that adapt to your existing processes rather than forcing teams into rigid approval models.
Organizations can:
- Configure up to three levels of approvers
- Assign individual users or user groups as approvers
- Create exclusion lists for trusted administrators
- Define automatic approval windows during specific business hours
- Allow users to request immediate access or schedule approvals for planned maintenance activities
Whether supporting IT operations, production changes, vendor maintenance, or emergency troubleshooting, approval workflows can be tailored to meet your organization's governance requirements.
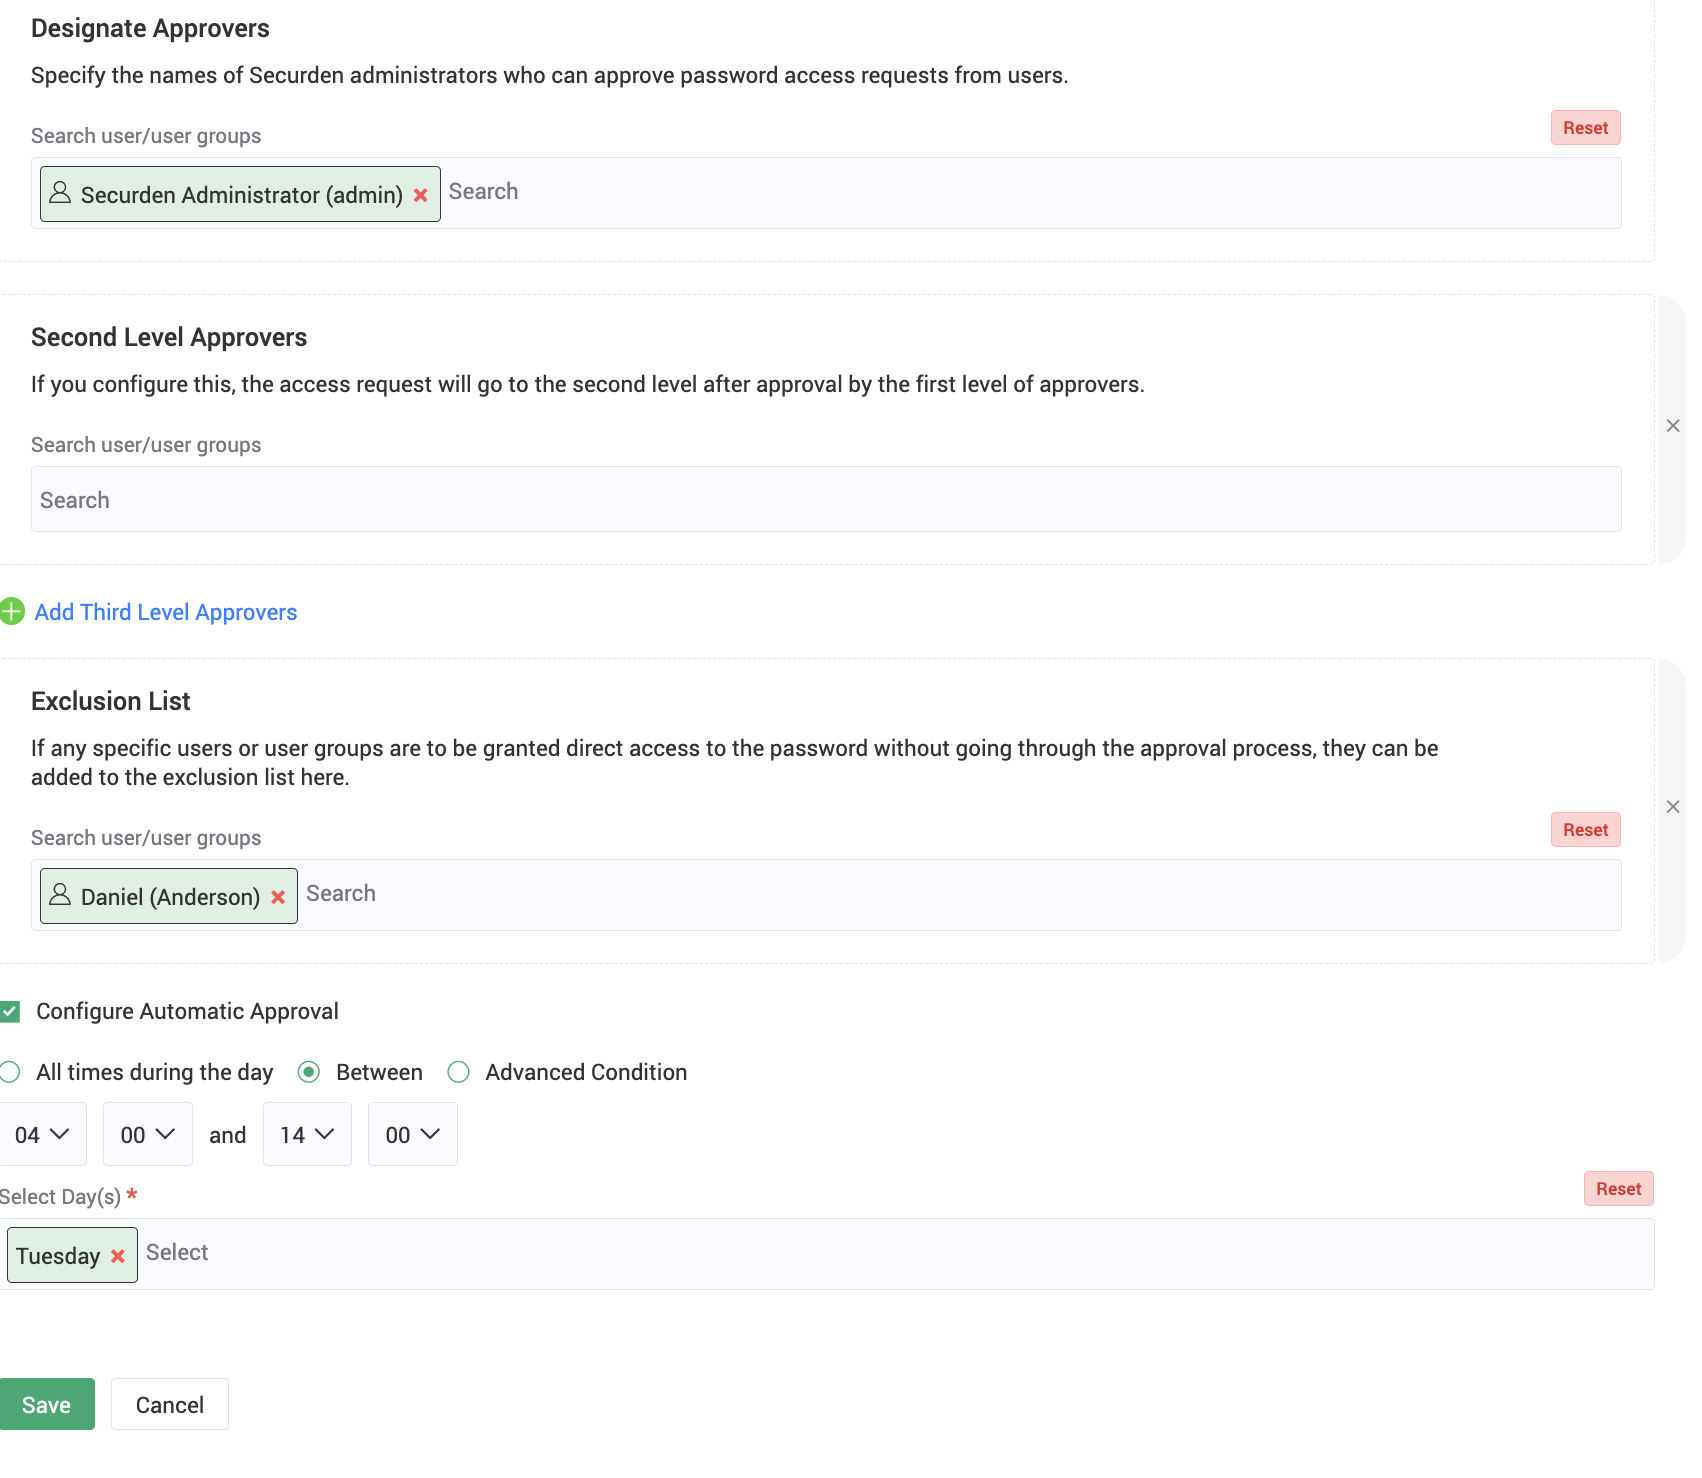
Keep Administrators in Complete Control
Securden Password Vault for Enterprises gives approvers complete visibility into every credential request and the flexibility to control access throughout its lifecycle. Before granting access, approvers can review the requester's business justification, adjust the requested duration, and add approval comments,
To strengthen accountability, Securden prevents concurrent access to shared accounts by allowing only one approved user to access a credential at a time. While access is active, the credential remains unavailable to other users—including administrators and account owners—until the session ends or access is revoked.
Administrators can revoke access at any time, even during an active session, ensuring shared credentials remain under continuous oversight while every privileged activity can be clearly attributed to an individual user.
Audit Every Credential Access
Securden Password Vault for Enterprises records who requested access, the business justification provided, who approved the request, the duration granted, when access began and ended, user activity patterns and so on.
Combined with detailed audit logs and user reports, organizations gain complete visibility into shared account usage while simplifying compliance reporting, security investigations, and internal audits.
Benefits at a Glance
|
Controlled Access through Approval Workflows Grant access to critical systems only when it's required instead of permanently exposing critical credentials. |
Prevent Shared Account Misuse Restrict concurrent access to critical systems and improve accountability for privileged activities. |
|
Enforce Least Privilege Require every credential request to be reviewed and approved before access is granted. |
Improve Audit Readiness Maintain complete records of privileged access requests, approvals, and credential usage for audits and investigations. |
|
Time-limited, Fully Audited Access Automatically revoke access once the approved access window expires. |
Balance Security with Productivity Enable administrators, developers, vendors, and contractors to obtain privileged access quickly without compromising governance. |
|
Custom Approval Workflows Configure multi-level approval workflows that align with your organization's operational and compliance requirements. |
Eliminate Standing Privileges Without Slowing Down IT
Secure shared credentials, enforce just-in-time access, prevent concurrent sessions, and maintain complete audit trails—all from a single enterprise password vault.

