- On-prem
- SaaS
Architecture: On-Premises Version
Securden Password Vault for Enterprises is a web-based, on-premises, self-hosted password management solution delivered as a single, self-contained software package for installation on Windows servers. The package includes all essential components, including an embedded web server and a bundled PostgreSQL database, eliminating the need for additional software dependencies. Microsoft SQL Server is also supported as an alternative database backend.
The solution follows a centralized architecture, with the application server managing business logic, authentication, access controls, and administrative operations. End users access the platform through standard web browsers, without requiring agents or additional software installations on their endpoints.
Vault Design, Encryption Standards, Key Management
Securden protects sensitive information through a fully encrypted vault using AES-256 encryption. Encryption is performed at the application layer before information is written to the database, ensuring that sensitive data remains protected at rest.
Each installation uses a uniquely generated encryption key. For enhanced security, the key can be stored separately from the application server, either in a protected network location accessed through a dedicated service account or within a connected Hardware Security Module (HSM).
All sensitive data at rest is protected using AES-256 encryption, while data transmitted during remote sessions and other remote operations is secured through TLS/SSL-encrypted communication channels.
Secure Remote Access
Password Vault for Enterprises enables authorized users to launch native and browser-based RDP, SSH, and SQL connections to servers, databases, and other IT resources. Credentials are supplied automatically, allowing users to connect without viewing or manually entering the underlying passwords. By default, these connections are routed through the Securden server, removing the need for direct connectivity between user devices and target systems.
For native connections, the Securden Remote Launcher installed on the user’s device opens the corresponding client application and automatically fills in the stored credentials. Permissions and approval workflows govern access, while audit trails capture connection launches and associated user and account details, supporting accountability and access reviews.
High Availability and Distributed Deployment
Securden supports a high-availability architecture (active-active model) comprising a primary application server and a standby secondary server, each maintaining its own database. Both servers operate concurrently, with encrypted streaming replication from the primary database to the secondary database, enabling the standby server to assume operations in the event of a primary server failure.
Read-only replica servers can also be deployed across distributed networks to facilitate password retrieval and remote connections, improving access efficiency and reducing dependence on a centralized deployment.
Together, these architectural capabilities provide centralized credential control, secure remote connectivity, high availability, distributed scalability, and strong data protection, supporting deployment in versatile customer environments.
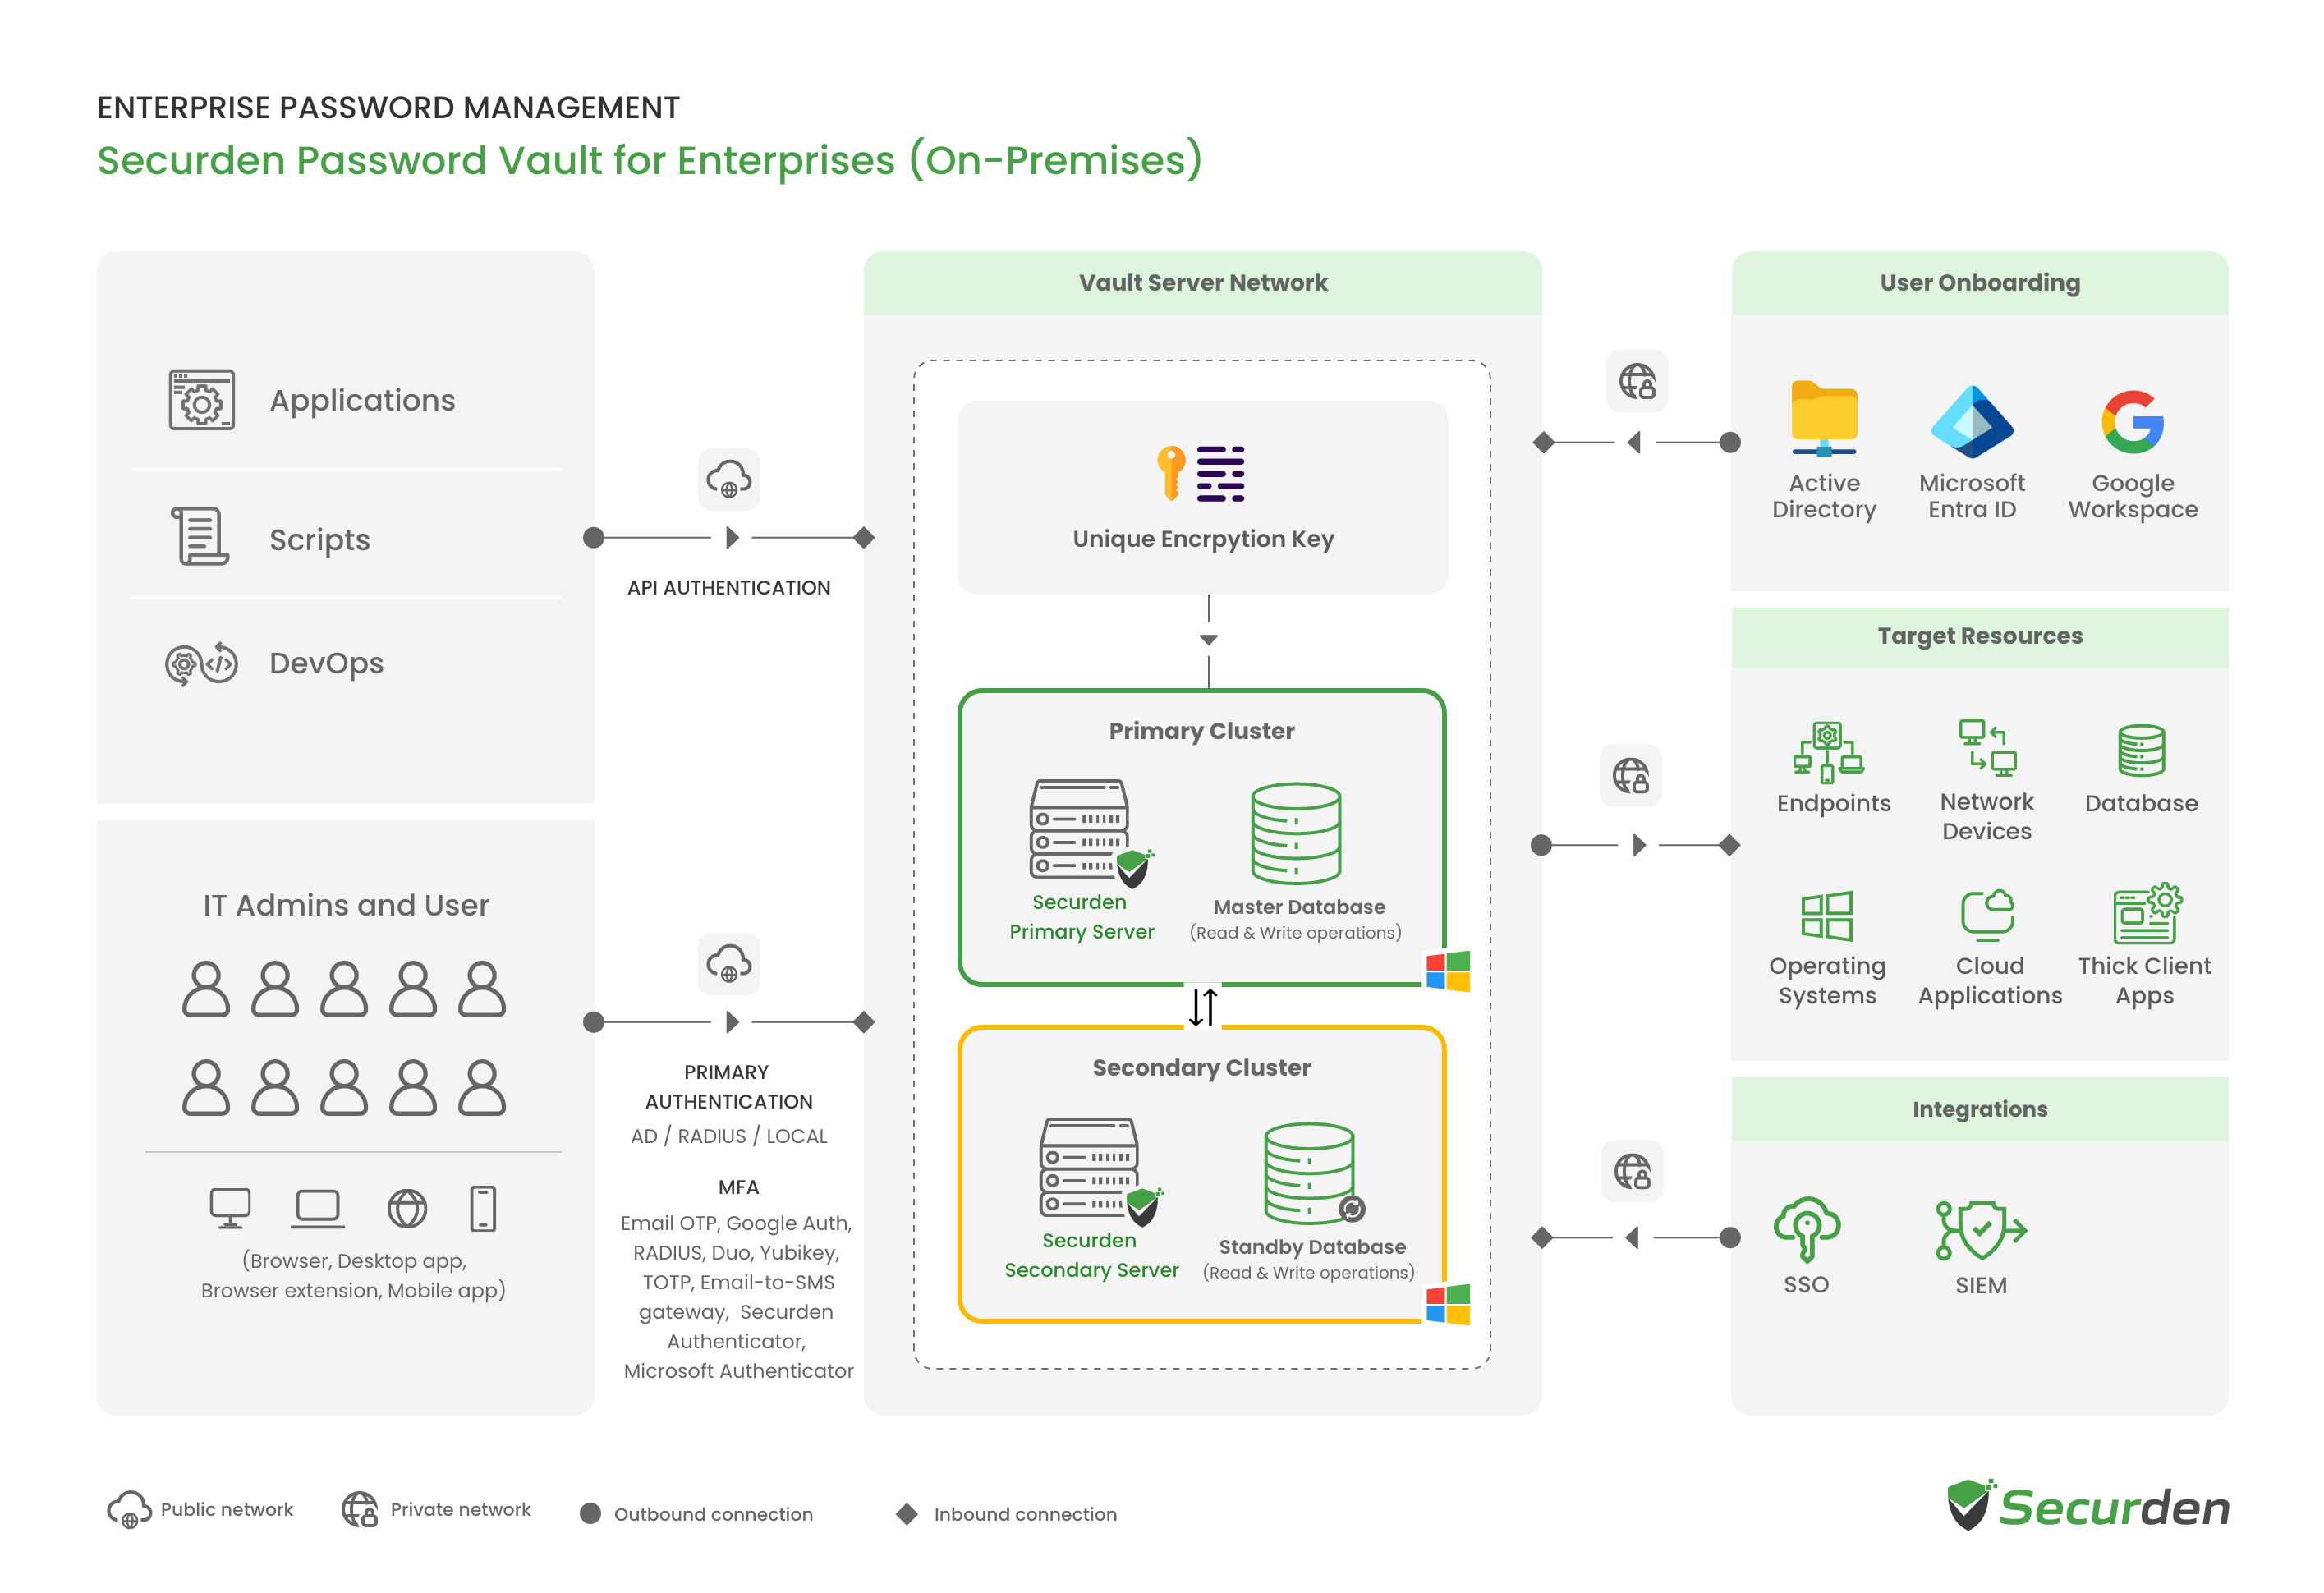
Core Components
Password Vault Application Server
The Password Vault application server hosts the web interface and core services. It processes user, API requests, enforces access permissions and approval policies, and coordinates credential operations with the database and integrated systems. Users connect through the web interface, desktop and mobile applications, and browser extensions, with HTTPS protecting communication with the server.
Database (Primary)
The database stores encrypted credentials, account information, configuration data, and audit records. Password Vault includes a bundled PostgreSQL database, with Microsoft SQL Server available as an alternative backend. The selected database determines the configuration and network connections required for the deployment.
Database (Secondary)
Organizations have the option to configure a secondary database to ensure always-on availability. The secondary database receives encrypted, asynchronous streaming replication from the primary database. If the primary Vault server becomes unavailable, the secondary server is automatically promoted, and its database becomes the master database to support continued access.
Encryption and Key Management
Sensitive vault data is encrypted at the application level using AES-256 before it is stored in the database. Each installation uses an automatically generated, unique encryption key. Administrators can protect the key separately from the Vault server using a secure storage location or a supported hardware security module (HSM). Communication with the Vault is protected using HTTPS and SSL/TLS.
User Onboarding
Users can be onboarded into Password Vault from Active Directory, Microsoft Entra ID, Google Workspace, and LDAP directories. Furthermore, manual and file-based user onboarding options are also available. Administrators assign users to roles and groups and configure granular permissions to control access to credentials and folders.
User Authentication
User authentication options include Active Directory, AD single sign-on (AD SSO), SAML-based single sign-on, RADIUS, passkey, and local Securden authentication. Administrators can enforce multi-factor authentication using supported methods, including TOTP authenticators such as Google Authenticator and Microsoft Authenticator, Duo, YubiKey, RADIUS-based services, email OTP, and email-to-SMS gateways.
Machine and Application Authentication
Applications, scripts, and DevOps workflows access the Vault’s APIs over HTTPS using API tokens or OAuth authentication. With OAuth, an application uses its client ID and client secret to obtain an access token programmatically and supplies that token with subsequent API requests. This enables credential retrieval and permitted Vault operations without hardcoding an access token. Access remains governed by the configured permissions and API scope.
Remote Connections
Web and Cloud Applications
Users can launch websites, web applications, and cloud services from Password Vault using the Securden browser extension. The target application opens in a separate browser tab, and the extension automatically fills the stored credentials into the sign-in fields, enabling access without manually entering or copying passwords.
Native and Browser-Based RDP, SSH, and SQL Connections
Authorized users can launch native and browser-based RDP, SSH, and SQL sessions to servers, databases, and other IT resources without viewing the underlying passwords. Native sessions use the Securden Remote Launcher installed on the user’s device to open the corresponding client application and supply credentials automatically. Browser-based sessions provide access through the browser. Permissions, approval workflows, and just-in-time (JIT) controls govern access to the target accounts.
Custom Application Launcher
Authorized users can create separate launcher profiles for thick-client, legacy, and other applications, defining each application’s launch and sign-in requirements. An administrator reviews and approves each profile before use. Once approved, users can launch the application in one click, with credentials supplied automatically and without viewing the underlying password.
Audit Trails and SIEM Integration
Audit Trails
Searchable audit trails record the user, account, and session activity, and the timeframe of credential access, administrative changes, connection launches, and API operations. Reports and event notifications support security reviews, investigations, and audits.
SIEM Integration
Organizations can forward audit events to their Security Information and Event Management (SIEM) platforms for centralized monitoring and correlation with other security activities.
Backup, Recovery, and Availability
Backup, recovery, and high availability capabilities support business continuity. Availability depends on the selected edition and deployment configuration. The High Availability section below describes in detail the primary and secondary servers, read-only replicas, and failover arrangements.
For more details about port configuration, refer here.
High Availability Architecture (On-Premises)
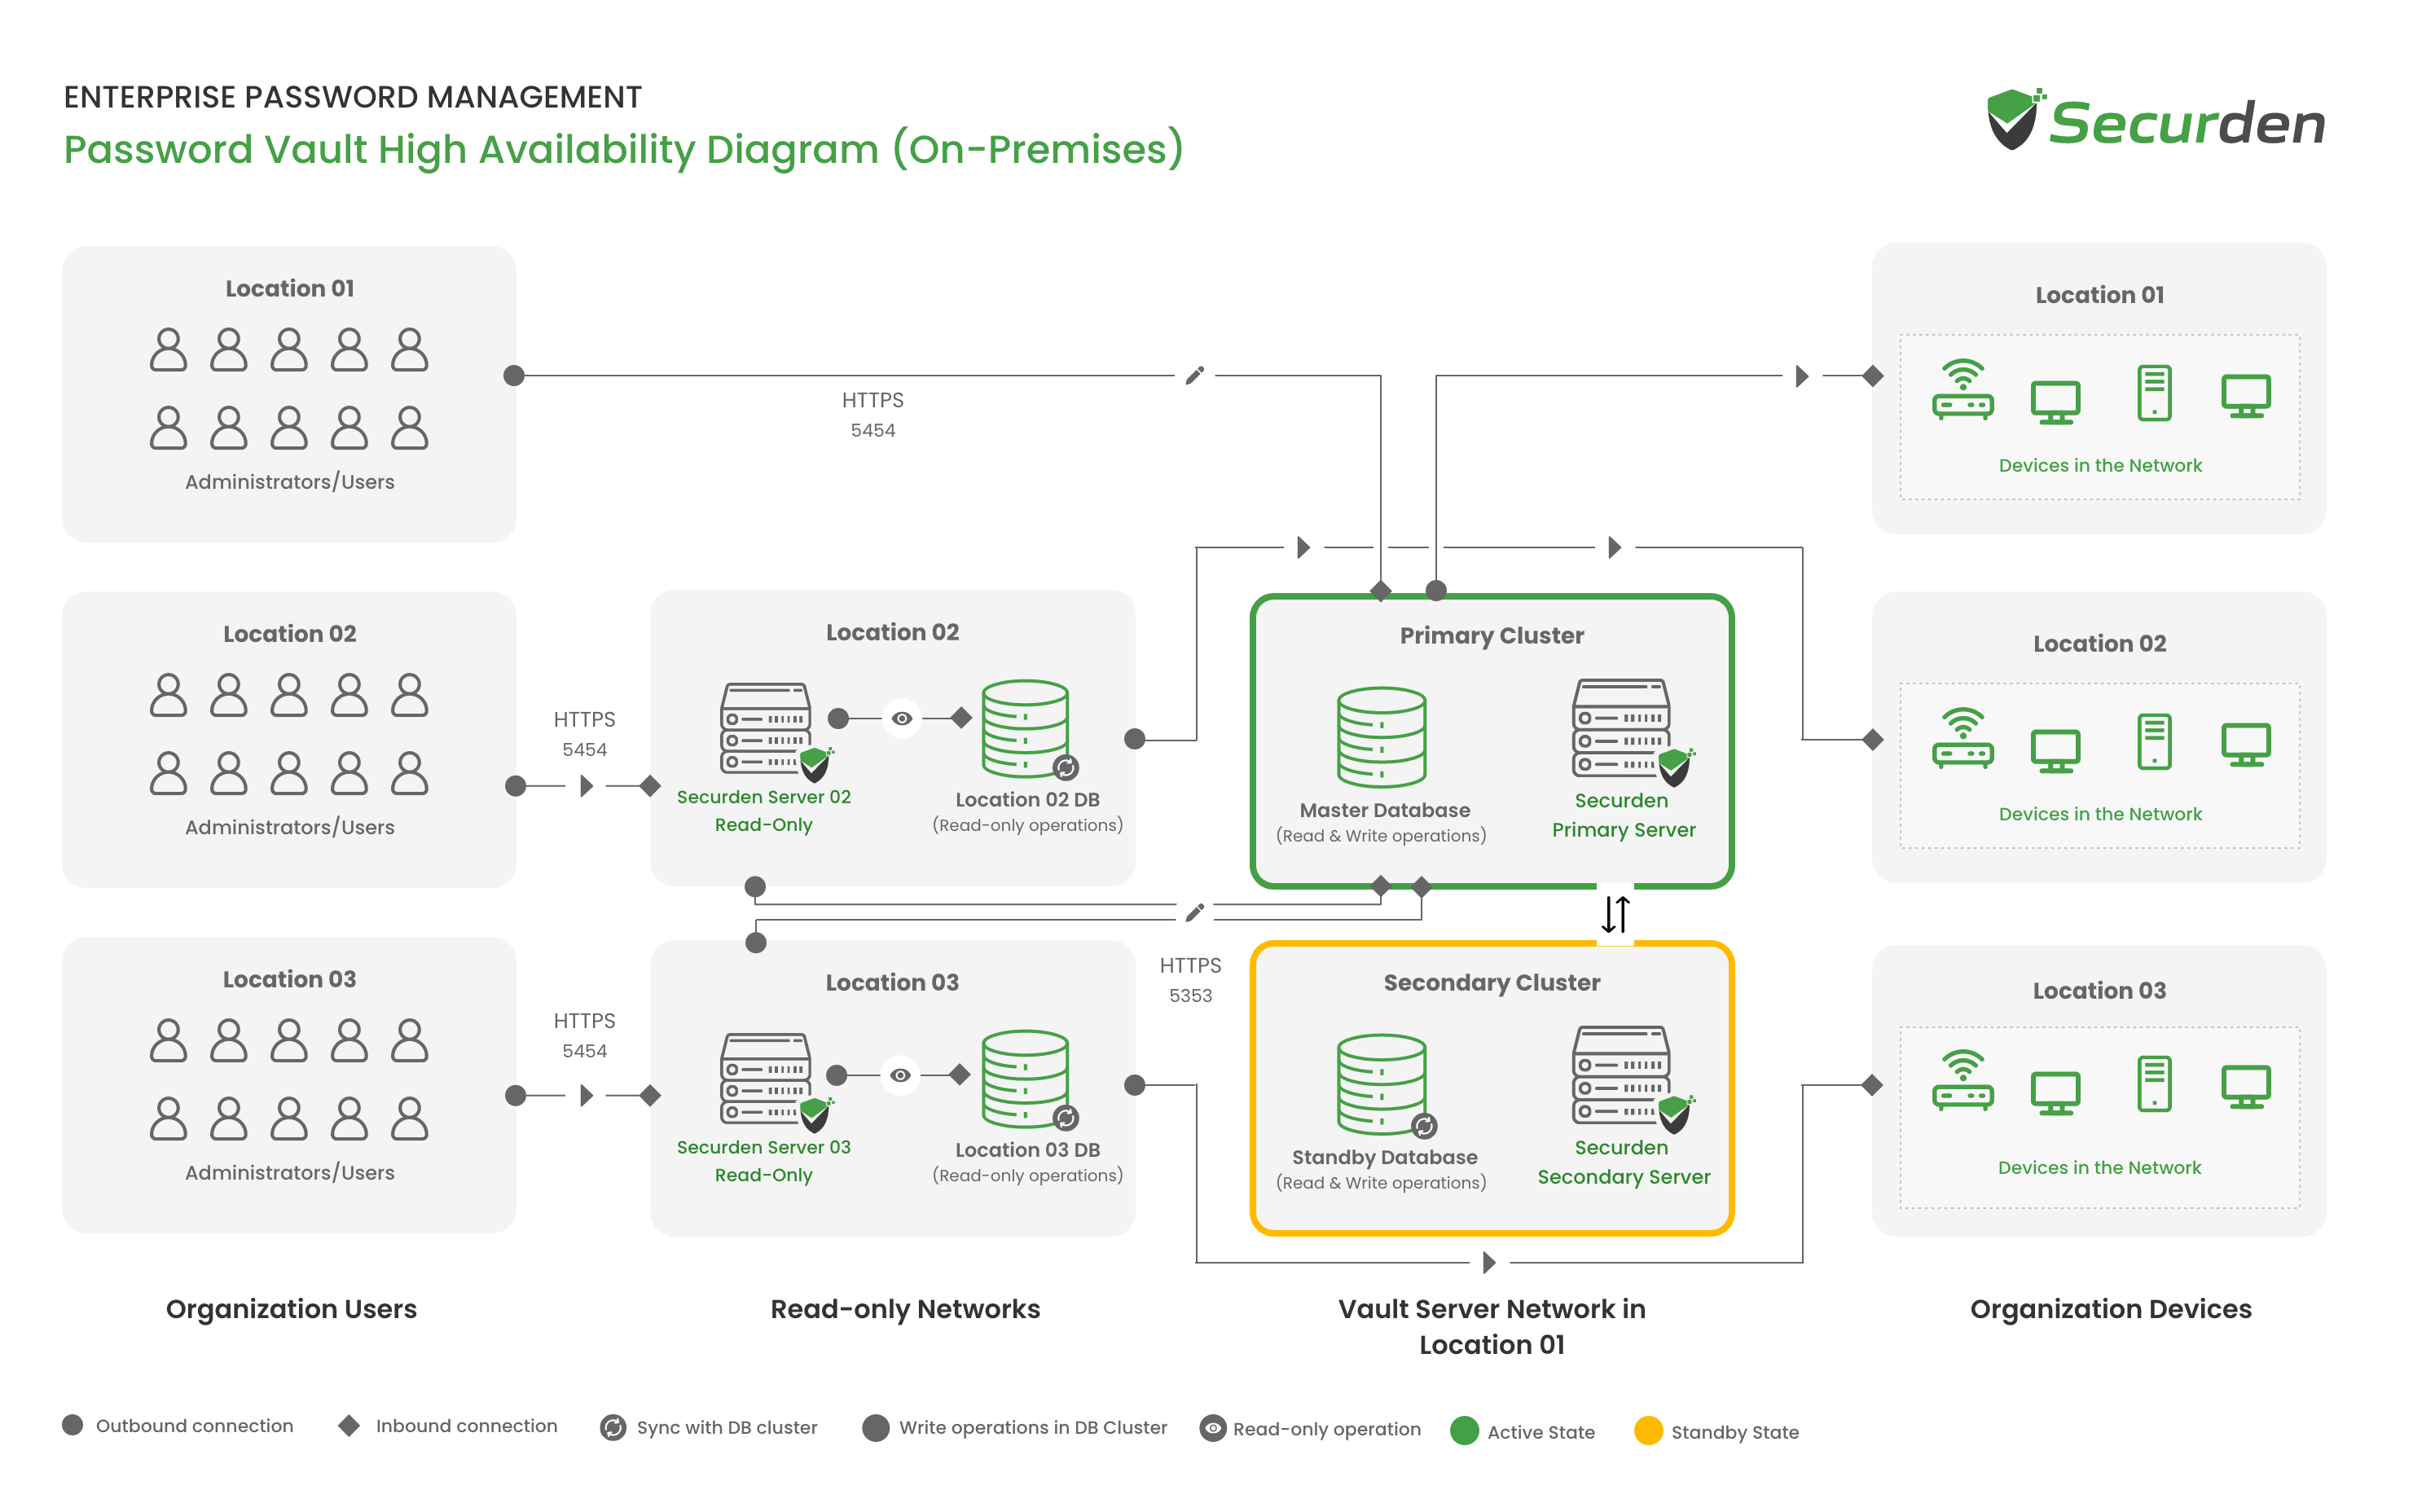
Securden Password Vault for Enterprises supports high availability (HA) for on-premises and self-hosted deployments through redundancy at both the application and database layers. The architecture combines primary and secondary application servers with corresponding PostgreSQL databases. Read-only replica servers provide an additional access path if both the primary and secondary servers become unavailable.
Primary Application Server
The primary application server operates as the active Password Vault server and receives user traffic during normal operations. It hosts the Password Vault web interface and core services, processes requests, enforces access permissions, and coordinates operations with the primary PostgreSQL database.
Secondary Application Server
The secondary application server remains on standby, ready to assume the active role if the primary application server becomes unavailable. It is associated with the secondary PostgreSQL database, which receives replicated data from the primary database. During failover, the secondary application server is promoted automatically and uses the promoted secondary database to continue Vault operations.
Primary Database
The primary PostgreSQL database serves as the master database, while the read-only server handles the read operations. The master database maintains the data used by the application server(s) and supplies replication data to the secondary database and read-only replicas.
Replication to the secondary database uses asynchronous, encrypted streaming replication, while read-only replicas receive data through synchronous replication. These replication paths support database redundancy and access through distributed replica servers.
Secondary Database
The secondary PostgreSQL database operates as a standby database and receives updates from the primary database. This maintains a replicated copy of the Vault data for use during failover.
When the primary server fails and the secondary application server is promoted, the secondary database assumes the primary database role. It becomes the active database for read and write operations, supporting continued service through the secondary application server.
Read-Only Replica Servers
Each read-only replica server includes an application server and a PostgreSQL replica database. Organizations can deploy multiple replicas across different locations according to their availability and access requirements. The replica databases receive data from the primary database through synchronous replication.
If both the primary and secondary servers become unavailable, users can sign in again to a read-only replica to retrieve passwords and launch remote connections using the last-synchronized data. Replicas reconnect automatically when both primary and secondary servers become unavailable.
Read-only replicas can also offload reporting and other read-heavy workloads from the primary. When configured appropriately by the organization, replicas can perform read requests such as password retrieval, and forward write requests received to the primary server.
Operations in Read-Only Mode
When Password Vault operates in read-only mode, users can continue to retrieve passwords, view account details, access audit records, and perform other read-only operations. However, any action that modifies data in the database is unavailable until normal read-write access is restored.
Important Note: All servers in the high availability configuration must run the same Password Vault version. Whenever the primary server is upgraded, every secondary and read-only replica server must also be upgraded to the same version.
Securden Password Vault for Enterprises centrally manages business credentials, providing employees, IT administrators, and authorized applications with controlled access to the passwords they need. Administrators define ownership, permissions, and approval requirements for storing, sharing, and using credentials. Users access the Vault through its web interface, desktop and mobile applications, and browser extensions, while applications and scripts use authenticated APIs. Audit trails provide visibility into credential access and administrative activity.
Password Vault supports on-premises, SaaS, and hybrid cloud deployments, allowing organizations to choose their preferred set up method.
Architecture: Cloud (SaaS) Version
The SaaS version of Password Vault for Enterprises provides the core credential management, authentication, access control, application launch, audit, and other capabilities through a Securden-managed service hosted in Amazon Web Services (AWS). Securden provisions, secures, operates, and maintains the hosted application and database infrastructure. Customers manage their users, permissions, authentication policies, and approval workflows without administering the hosted servers or databases.
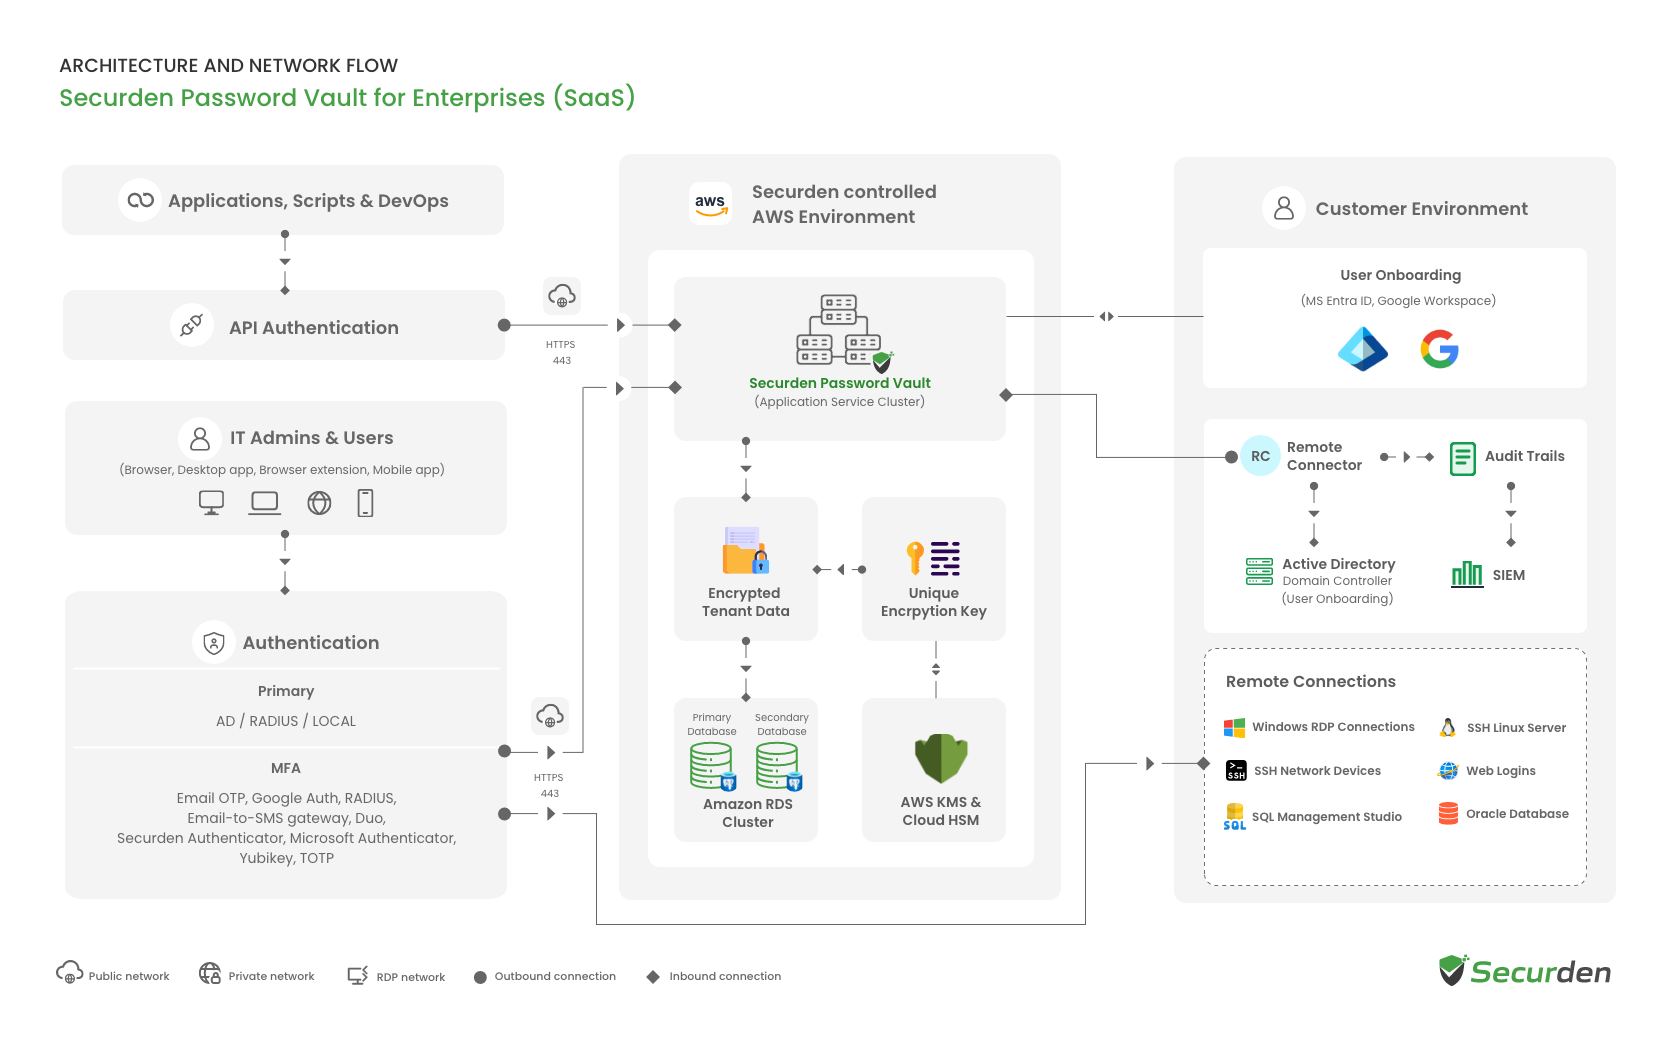
The following components and connection arrangements differ from an on-premises deployment.
Core Components
Application Server
The primary application server hosts the Password Vault web interface and core services, processes user and API requests over HTTPS, and enforces permissions and approval policies. A secondary application server provides redundancy and supports continued availability if the primary becomes unavailable. Securden manages both servers, their redundancy configuration, maintenance, and recovery. Customers do not need to deploy, maintain, or switch between application servers.
Primary Database
The primary database is hosted on Amazon RDS for PostgreSQL and stores segregated, encrypted customer data. Securden manages database provisioning, configuration, security controls, backups, and ongoing maintenance. Customers do not need to deploy or administer the database. The secondary database is kept continuously synchronized with the primary through replication. If the primary becomes unavailable, the database service automatically switches to the secondary. Again, Securden manages the secondary database, replication, maintenance, and automatic failover configuration.
Encryption and Key Management
Customer data is encrypted at the application level using AES-256. Each customer has a unique encryption key managed through AWS Key Management Service (KMS), with AWS CloudHSM protecting the key material. Securden manages the hosted key infrastructure, while HTTPS and SSL/TLS protect data in transit.
Remote Connector
A Remote Connector is deployed within the customer environment connects the cloud-hosted Securden server with on-premises Active Directory and local target systems and forwards audit events to the customer’s local SIEM system if configured. The connector initiates an outbound HTTPS connection to the hosted server on TCP 443, requiring no Internet-facing inbound ports open in the customer network.
Microsoft Entra ID and Google Workspace support user onboarding through direct integrations with the cloud-hosted Securden server, without requiring to deploy a separate remote connector in the customer environment. Only On-premises Active Directory user onboarding utilizes the Remote Connector.
Remote Connections
Web and Cloud Applications
Users can launch web applications and cloud services directly from the Password Vault using the Securden browser extension. The target web application opens in a new browser tab, and the extension automatically fills the stored credentials into the sign-in fields, enabling access without manually entering or copying passwords.
Native RDP, SSH, and SQL Connections
Users launch native RDP, SSH, and SQL sessions through the lightweight Securden Remote Launcher installed on their devices. The launcher opens the corresponding native client application, with credentials supplied automatically to establish the authorized connection.
Custom Application Launcher
Authorized users can create separate launcher profiles for thick-client, legacy, and other applications, defining each application’s launch and sign-in requirements. An administrator reviews and approves each profile before use. Once approved, users can launch the application in one click, with credentials supplied automatically and without viewing the underlying password.
Audit Trails & Events
The Remote Connector periodically forwards audit events to the customer’s SIEM platform. For SIEM platforms deployed within the customer environment, the Remote Connector periodically forwards audit events to the configured SIEM listener. For cloud-hosted SIEM platforms, the cloud-hosted Securden server forwards audit events directly. Administrators can choose to forward all activities or specific event types for centralized monitoring and correlation with other security data.
For more details about port configuration, refer here.