Architecture Overview
Securden Unified PAM: MSP Edition is an on-premises, self-hosted, multi-tenant solution that enables managed service providers to deliver privileged access management as a service (PAMaaS) to multiple client organizations from a single deployment. MSPs can deliver fully managed services or share administration with client IT teams through a co-managed model.
Each client organization has a separate administrative boundary, with its privileged access data kept segregated from other organizations. Administrators, roles, policies, approval workflows, MFA, and enabled features can be configured independently for each client.
The software-only solution is delivered as a single binary package for installation on Windows, with an inbuilt web server and a bundled PostgreSQL database. Microsoft SQL Server can alternatively be configured as the backend database.
The central PAM server handles the application’s business logic, and users access the web interface over HTTPS through a standard browser without installing client software for web access. The primary and secondary PAM servers are hosted in the MSP environment. Client privileged systems can reside within client networks, within the MSP network, or across both. A single PAM MSP instance supports these deployment scenarios simultaneously.
Remote Connectors provide connectivity between the PAM server and client privileged systems. A connector deployed within a client network establishes an outbound Secure WebSocket connection to the PAM server, eliminating the need to open inbound ports in the client firewall for this connection. Remote Connectors also route connections to client assets located within the MSP network.
For remote connections, session management, and recording, Securden uses a gateway model based on Securden Session Manager (SSM). Deployed on a jump host within the network, SSM brokers RDP, SSH, and SQL connections between end-user machines and target resources. Remote sessions routed through this gateway avoid direct connectivity between end-user machines and sensitive IT assets.
Data belonging to each client organization is stored in the database and kept segregated from that of other organizations. Users from a client organization can access only the assets belonging to their own organization.
High availability is supported through primary and secondary PAM servers. Additional application servers can provide load distribution across distributed or multi-site networks, while read-only replica servers can support password retrieval and remote connections in distributed environments.
Sensitive information is stored in an AES-256-encrypted vault. Encryption is performed at the application level before data is stored in the database, using an automatically generated encryption key unique to each installation. The key can be protected in a separate network location accessed through a dedicated service account, or in a mounted physical Hardware Security Module (HSM).
Data at rest is encrypted using AES-256. Data in transit during remote sessions and remote operations is encrypted using TLS/SSL and transmitted over secure channels.
Core Components
| Component | Role |
|---|---|
| Primary PAM Server | Hosts the web console, core services, and PAM operations in the MSP environment. |
| Backend Database | Stores PAM data. PostgreSQL is bundled by default; Microsoft SQL Server can optionally be configured. Data belonging to each organization is kept segregated from that of other organizations. |
| Remote Connector | Connects the PAM server with client privileged systems and supports remote functions such as password reset, password verification, and account discovery. It communicates with the PAM server over Secure WebSocket. |
| Securden Session Manager (SSM) / Remote Gateway | Launches and records remote sessions between users and target machines. |
| API Server | Supports remote password reset, password verification, account discovery, and other remote functions. |
| Secondary PAM Server | Hosted in the MSP environment to support high availability. |
| Application Servers (optional) | Additional servers deployed for load distribution and to support distributed or multi-site networks from the central installation. |
| Read-Only Replica Servers (optional) | Deployed in distributed networks to provide reporting, password retrieval, and remote connections. These functions remain available even if one or both of the primary and secondary PAM servers are unavailable. |
Module Deployment Scenarios
Password Vault Module
The Password Vault module establishes centralized privileged credential management. Users securely access the vault over HTTPS. Data belonging to each client organization is kept segregated, and client users can access only the assets belonging to their organization.
Core PAM: Privileged Accounts, Sessions, and Access Control
Core PAM capabilities include session routing through Securden Session Manager (SSM). Privileged access to servers, databases, and network devices is managed through controlled workflows, with monitoring, recording, and audit trails.
MSP Deployment Across Client Environments
The primary and secondary PAM servers are hosted in the MSP environment. Client privileged systems can reside within client networks, within the MSP network, or across both. A single PAM MSP instance can support these deployment scenarios simultaneously.
Remote Connectors provide connectivity between the PAM server and client privileged systems over Secure WebSocket. Connectors deployed within client networks establish outbound connections to the PAM server, eliminating the need to open inbound ports in the client firewall for this connection.
High Availability and Disaster Recovery
The deployment includes high-availability and disaster-recovery configurations.
Module Configuration and Enablement
| Capabilities | Activities Performed |
|---|---|
| Password Vault | |
| Centralized encrypted credential storage, password randomization, and ownership controls | Configure the vault hierarchy and folder structures, enforce password complexity and rotation policies, define ownership and access controls, and enable credential expiration alerts. |
| Account Discovery | |
| Automatic discovery of privileged accounts across servers, databases, and network devices | Perform discovery scans, import discovered accounts into the vault, assign ownership, and onboard privileged accounts from target systems. |
| Session Management | |
| One-click remote privileged access through RDP, SSH, SQL, and HTTPS; live monitoring and recording | Deploy and configure Securden Session Manager instances to support high availability and load-balanced privileged session routing. Enable session recording, define retention policies, enforce session controls, and validate connectivity across infrastructure systems. |
| Remote Operations Layer | |
| Password resets, password verification, account synchronization, and privileged automation | Configure connectors for account discovery, password rotation, verification workflows, and integration with Active Directory / Microsoft Entra ID. |
| Just-in-Time (JIT) Access | |
| Time-bound privilege elevation with approvals and automatic revocation | Configure approval hierarchies, justification requirements, time-bound access policies, and automatic privilege revocation workflows for sensitive administrative operations. |
| Privileged Session Analytics | |
| Session tracking, anomaly detection, and usage monitoring | Enable session-level reporting, privileged activity insights, anomaly alerts, and administrator behavior monitoring dashboards. |
| Integration Layer | |
| Active Directory, SSO through SAML 2.0, MFA, SIEM, and ITSM integrations | Establish and validate integrations with Active Directory / Microsoft Entra ID, configure SAML-based SSO, enforce MFA, and enable SIEM log forwarding and webhook-based event notifications. |
| Security Hardening | |
| Encryption, MFA enforcement, role-based access controls, and IP restrictions | Apply security controls, including enforced MFA, RBAC policies, IP-based access restrictions, administrative lockdown rules, and secure operational boundaries for privileged users. |
| Audit and Reporting | |
| Compliance reporting, event notifications, and audit trails | Configure tamper-proof audit logging, scheduled compliance reports, privileged access dashboards, retention policies, and automated alerting mechanisms. |
| Multi-Tenant Data Segregation | |
| Segregation of organization data and organization-specific asset access | Maintain segregation of each client organization’s data and restrict client users to assets belonging to their own organization. |
| Remote Connector | |
| Connectivity between the central PAM server and client privileged systems; password reset, password verification, and account discovery | Deploy Remote Connectors within client networks to establish outbound Secure WebSocket connections to the PAM server. Use Remote Connectors to route connections to client assets within the MSP network, as illustrated in the deployment scenarios. |
| Client Asset Deployment | |
| Support for client privileged systems located in client networks, the MSP network, or both | Set up connectivity according to the location of each client’s privileged systems. Support these deployment scenarios simultaneously through a single PAM MSP instance. |
Component Configuration and Connectivity
Remote Connector
For privileged systems located within a client network, a Remote Connector is deployed within that network. The connector establishes an outbound Secure WebSocket connection to the PAM server in the MSP environment. Inbound access to the client network is not required for this connection.
The deployment scenarios also illustrate Remote Connectors routing connections to client assets located within the MSP network.
Session Management and Remote Operations
To enable remote connections and certain remote functions across multiple networks, Securden Session Manager, the API Server, or both can be deployed on the machine serving as the Remote Gateway.
If the requirement is limited to remote session launch and recording, SSM alone is sufficient. If remote password reset is required, an Application Server must also be associated with the gateway.
Directory and Authentication Integrations
Connectivity requirements depend on the integrations configured for the deployment. These can include Active Directory, Microsoft Entra ID, and RADIUS-based authentication.
Active Directory connectivity uses port 636 TCP with SSL/TLS by default. Port 389 TCP is used only when SSL/TLS is not enabled. Microsoft Entra ID integration requires connectivity through Graph API over HTTPS.
Email Notifications
An external mail server must be configured and integrated with Securden Unified PAM: MSP Edition for users to receive email notifications.
SSL Certificate
A publicly trusted SSL certificate must be installed on the application server to authenticate and encrypt connections between user devices and the PAM server. The certificate configuration requires the SSL certificate, corresponding private key, and intermediate Certificate Authority bundle.
Network and Port Requirements
The following ports support communication between the PAM servers, database, end-user machines, Securden Session Manager, and target systems.
| Port / Function | Source | Destination | Port / Protocol |
|---|---|---|---|
| PostgreSQL database Default backend database connectivity |
Primary, secondary, and all application servers | PostgreSQL server | 5758 TCP |
| Microsoft SQL Server database Required when Microsoft SQL Server is configured as the backend database |
Primary and application servers | Microsoft SQL Server | 1433 TCP |
| PAM web access — primary server Web port; can be changed if required |
Users, end-user machines, agents, and secondary servers | Primary PAM server | 5656 TCP |
| PAM web access — secondary server Web port; can be changed if required |
Users, end-user machines, agents, and secondary servers | Secondary PAM server | 5656 TCP |
| SSM inbound RDP RDP connectivity from client machines to SSM |
Client machines | SSM server | 3389 TCP |
| SSM outbound RDP RDP connectivity from SSM to target machines |
SSM server | Target machines | 3389 TCP |
| Browser-based SSH Browser-based SSH connections |
End-user machines | Application servers | 5722 TCP |
| Browser-based RDP Browser-based RDP connections |
End-user machines | Application servers | 5726 TCP |
| Web application session recording Browser-extension session recording, where supported |
Browser Extension Component | All application servers | 5836 TCP |
| SMTP — TLS Email notifications using TLS |
Application servers | Mail server | 587 TCP |
| SMTP — SSL Email notifications using SSL |
Application servers | Mail server | 465 TCP |
Note: The PAM web port can be changed based on deployment requirements.
Integration and Discovery Connectivity
| Function | Port or Connectivity Requirement |
|---|---|
| Active Directory using SSL/TLS | 636 TCP |
| Active Directory without SSL/TLS | 389 TCP |
| RADIUS-based authentication | 1812 UDP/TCP |
| Microsoft Entra ID integration | Graph API over HTTPS |
| Windows account discovery using WMI | 135 TCP |
| Linux, Cisco, and Mac discovery using SSH | 22 TCP, or the configured SSH port specified during discovery |
| PostgreSQL, SQL Server, Oracle, and MySQL discovery | Database ports specified during discovery |
| Remote Connector communication with PAM server | Outbound Secure WebSocket connection |
Data Flow
User Access to the Vault
- Users open the Securden web interface in a standard browser over HTTPS (no client software required). Access is also available via desktop and mobile applications.
- The primary server (or an application server) processes the request and applies role-based access, approval workflows, and MFA.
- Credentials are read from the backend database. Stored using AES-256 encryption, decryption occurs exclusively at the application level on the server.
Remote Privileged Sessions
- A user launches a one-click RDP, SSH, or SQL connection from the web interface.
- The request is routed to the Securden Session Manager on the jump host. All remote connections go through this gateway.
- The SSM brokers the connection to the target resource, ensuring no direct connectivity between the user's machine and the sensitive asset.
- The session is monitored live and recorded. Audit trails and analytics are generated from it.
- Data in transit during remote sessions and remote operations is encrypted with TLS/SSL and sent only over secure channels.
Remote Operations and Discovery
- The Remote Operations Layer performs password resets, verification, and account synchronization on target systems.
- Discovery connects to Windows hosts over WMI, and to Linux, Cisco, and Mac devices over SSH. For databases, specific database ports are targeted at scan time.
- Discovered accounts are imported into the vault and assigned ownership.
Replication and Distribution
- The primary server streams encrypted database replication to the secondary standby, which takes over if the primary fails.
- Application servers (without a local database) connect to the central database to share load across sites.
- Read-only replicas serve password retrieval and remote connections locally in distributed networks.
Communication with Client Privileged Systems
Users from client organizations connect to the PAM server in the MSP environment over HTTPS using a web browser. Users can access only the assets belonging to their own organization.
The PAM servers communicate with the backend database through the configured database port.
The communication path depends on the location of the client’s privileged systems:
- Client assets in the client network: The PAM server communicates with privileged systems through a Remote Connector deployed within the client network via an outbound Secure WebSocket connection.
- Client assets in the MSP network: Connections between the PAM server and each client’s privileged systems are routed through a Remote Connector communicating with the PAM server over Secure WebSocket.
- Client assets across both networks: Remote Connectors deployed within client networks provide connectivity to assets in those networks, alongside Remote Connectors routing connections to client assets within the MSP network.
Remote Sessions
Securden Session Manager launches and records remote sessions between users and target machines. When SSM is used for RDP connections, connectivity uses port 3389 from the client machine to SSM and from SSM to the target machine. Browser-based SSH and RDP connections use ports 5722 and 5726 respectively.
Discovery and Remote Operations
Remote Connectors support password reset, password verification, and account discovery. Windows account discovery uses WMI connectivity. Discovery of Linux, Cisco, and Mac systems uses SSH. Database discovery uses the database ports specified when performing discovery.
Data Protection Summary
| Area | Protection |
|---|---|
| At Rest | AES-256, applied at the application level before storage |
| In Transit | TLS/SSL over secure channels |
| Key Management | Unique per-installation key, stored on a separate network location via a dedicated service account, or in an HSM |
| Organization Data Segregation | Data belonging to each organization is stored in the database and kept segregated from that of other organizations. |
| Client Access Boundaries | Users from a client organization can access only the assets belonging to their organization, preventing access to other clients’ assets. |
| User-to-Server Communication | Users access the PAM server over HTTPS. A publicly trusted SSL certificate authenticates and encrypts connections between user devices and the application server. |
| Remote Connector Communication | The Remote Connector communicates with the PAM server over Secure WebSocket. For connectors deployed within client networks, the connection is outbound and does not require inbound access to the client network. |
Securden PAM: MSP Edition Deployment Architecture
Securden Unified PAM: MSP Edition supports three PAMaaS deployment scenarios based on the location of client privileged systems and how they are controlled and managed.
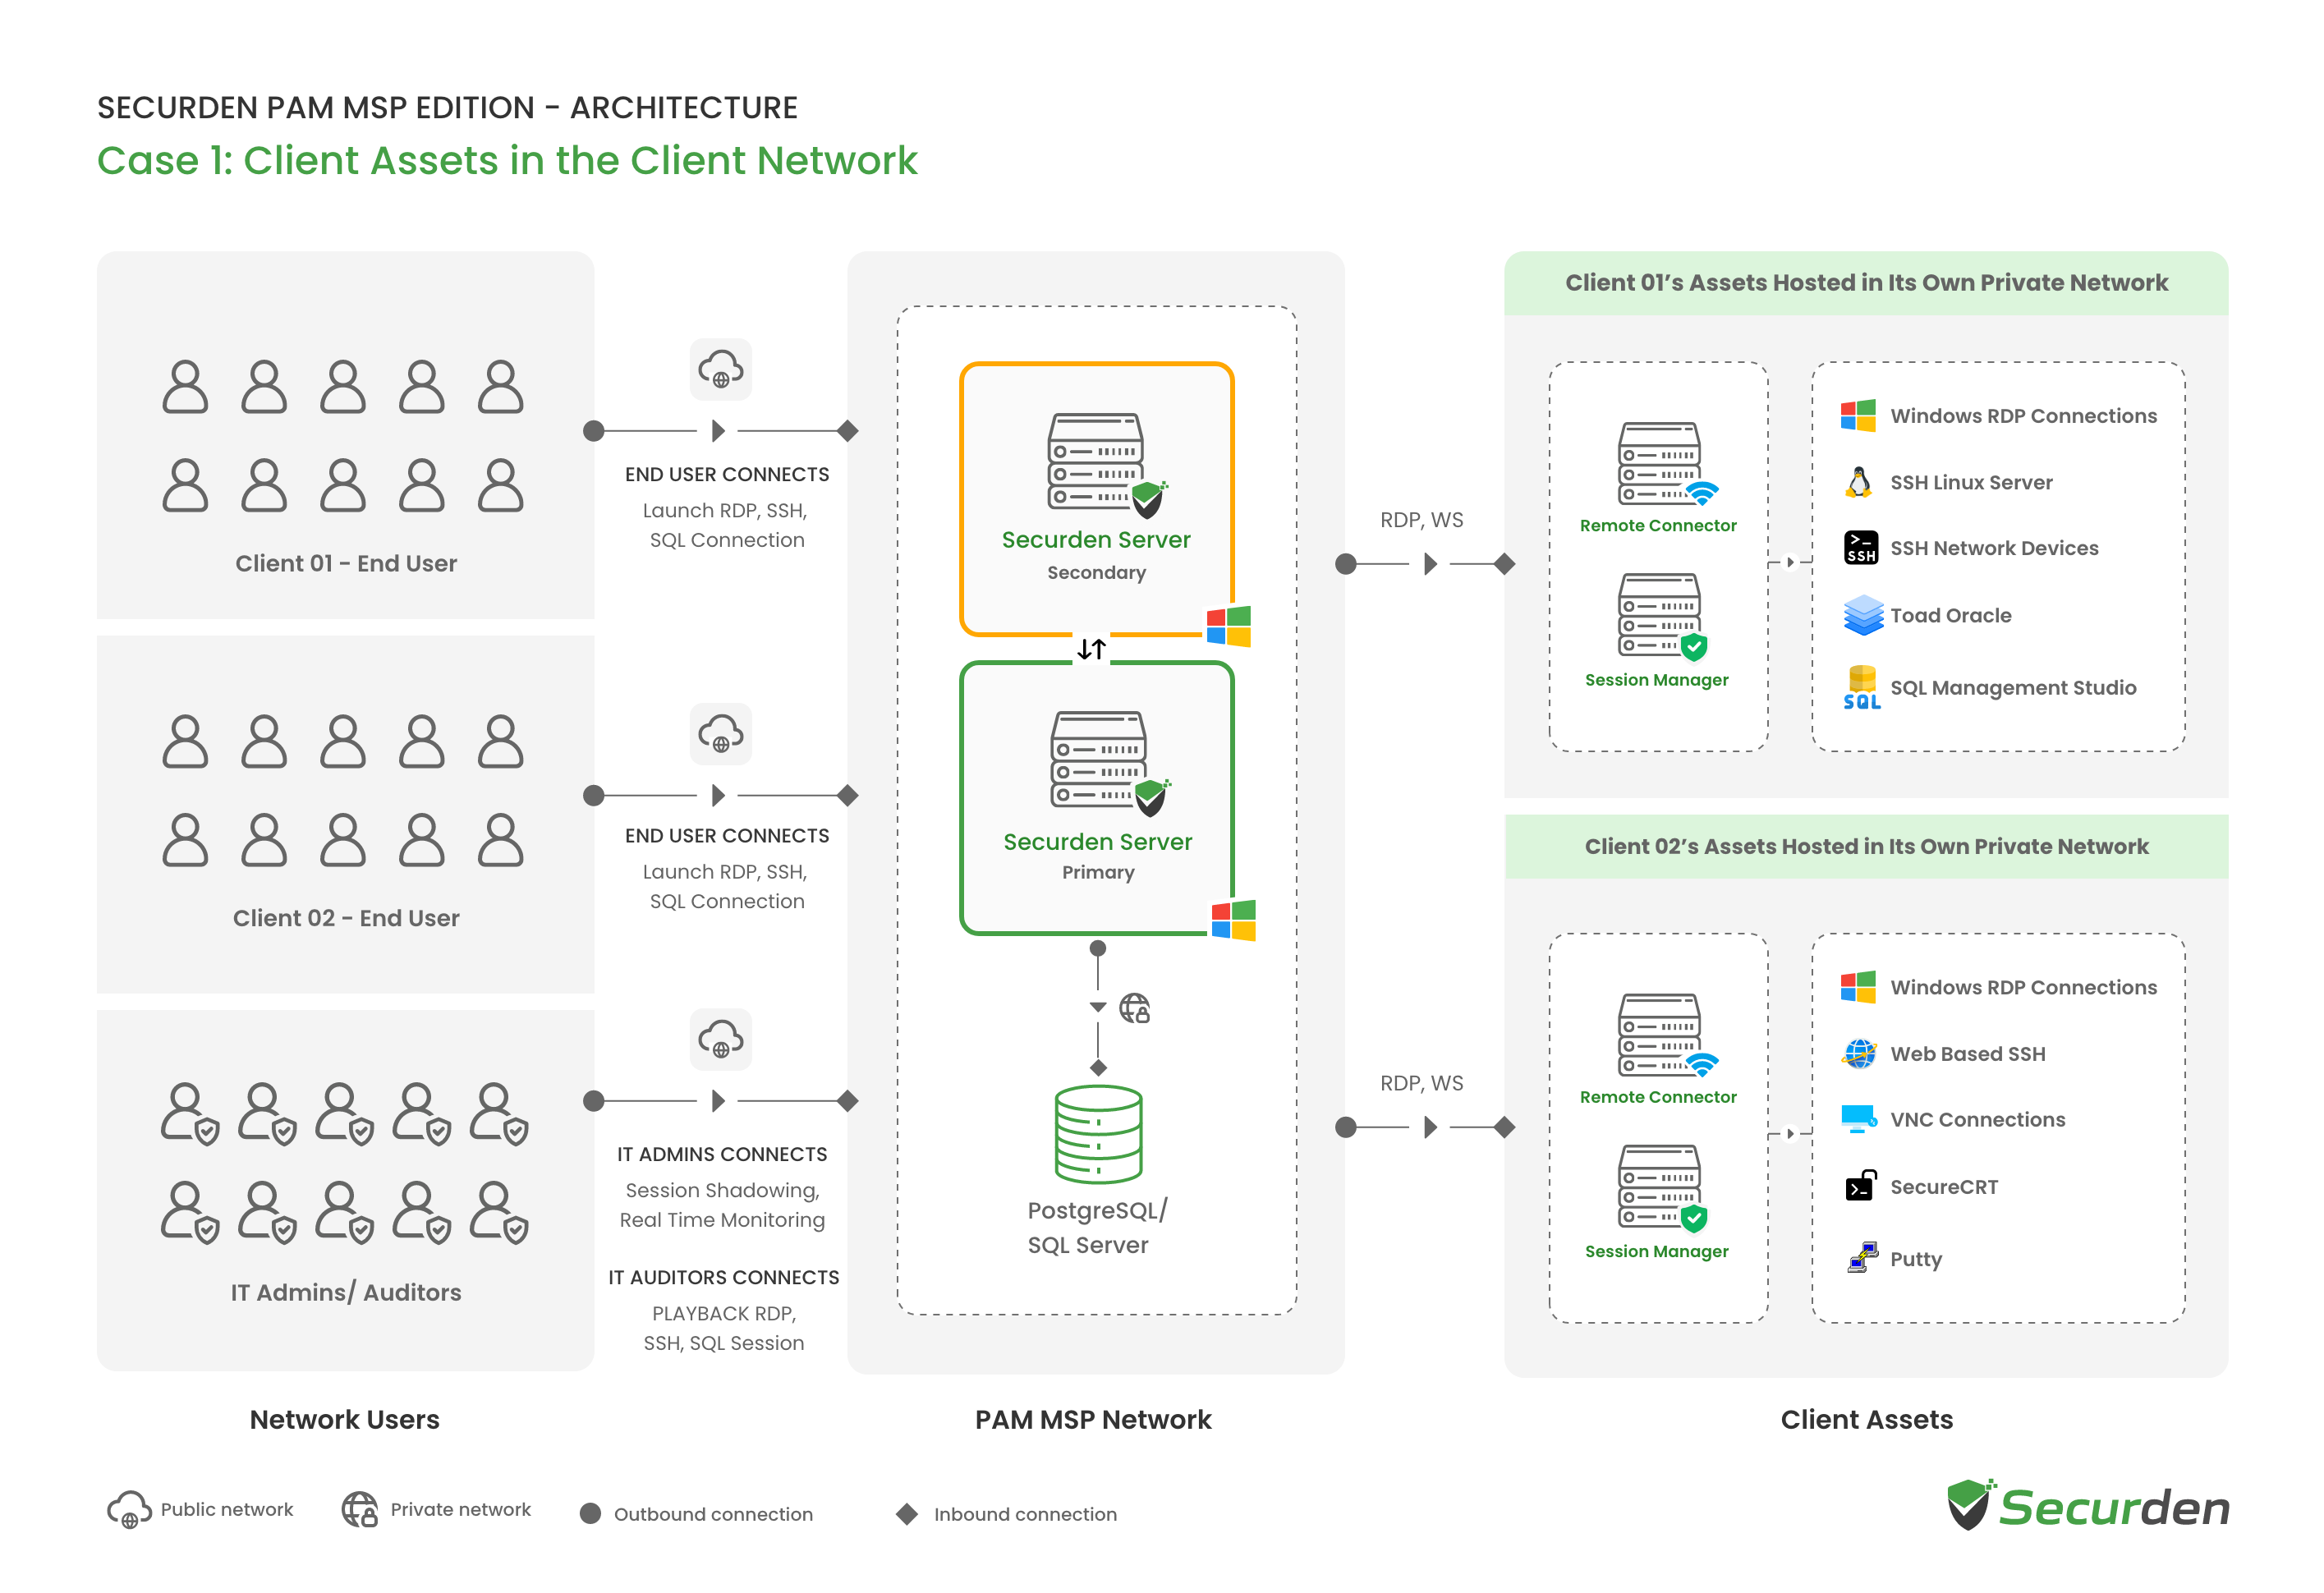
Case 1: Client Assets in the Client Network
The client's privileged systems reside within its own network. Users from the client organization access their authorized systems through the PAM Server. The PAM server in the MSP network communicates with the client's privileged systems through a Remote Connector deployed within the client network. The Remote Connector establishes an outbound Secure WebSocket connection to the PAM server, eliminating the need to open inbound ports in the client's firewall.
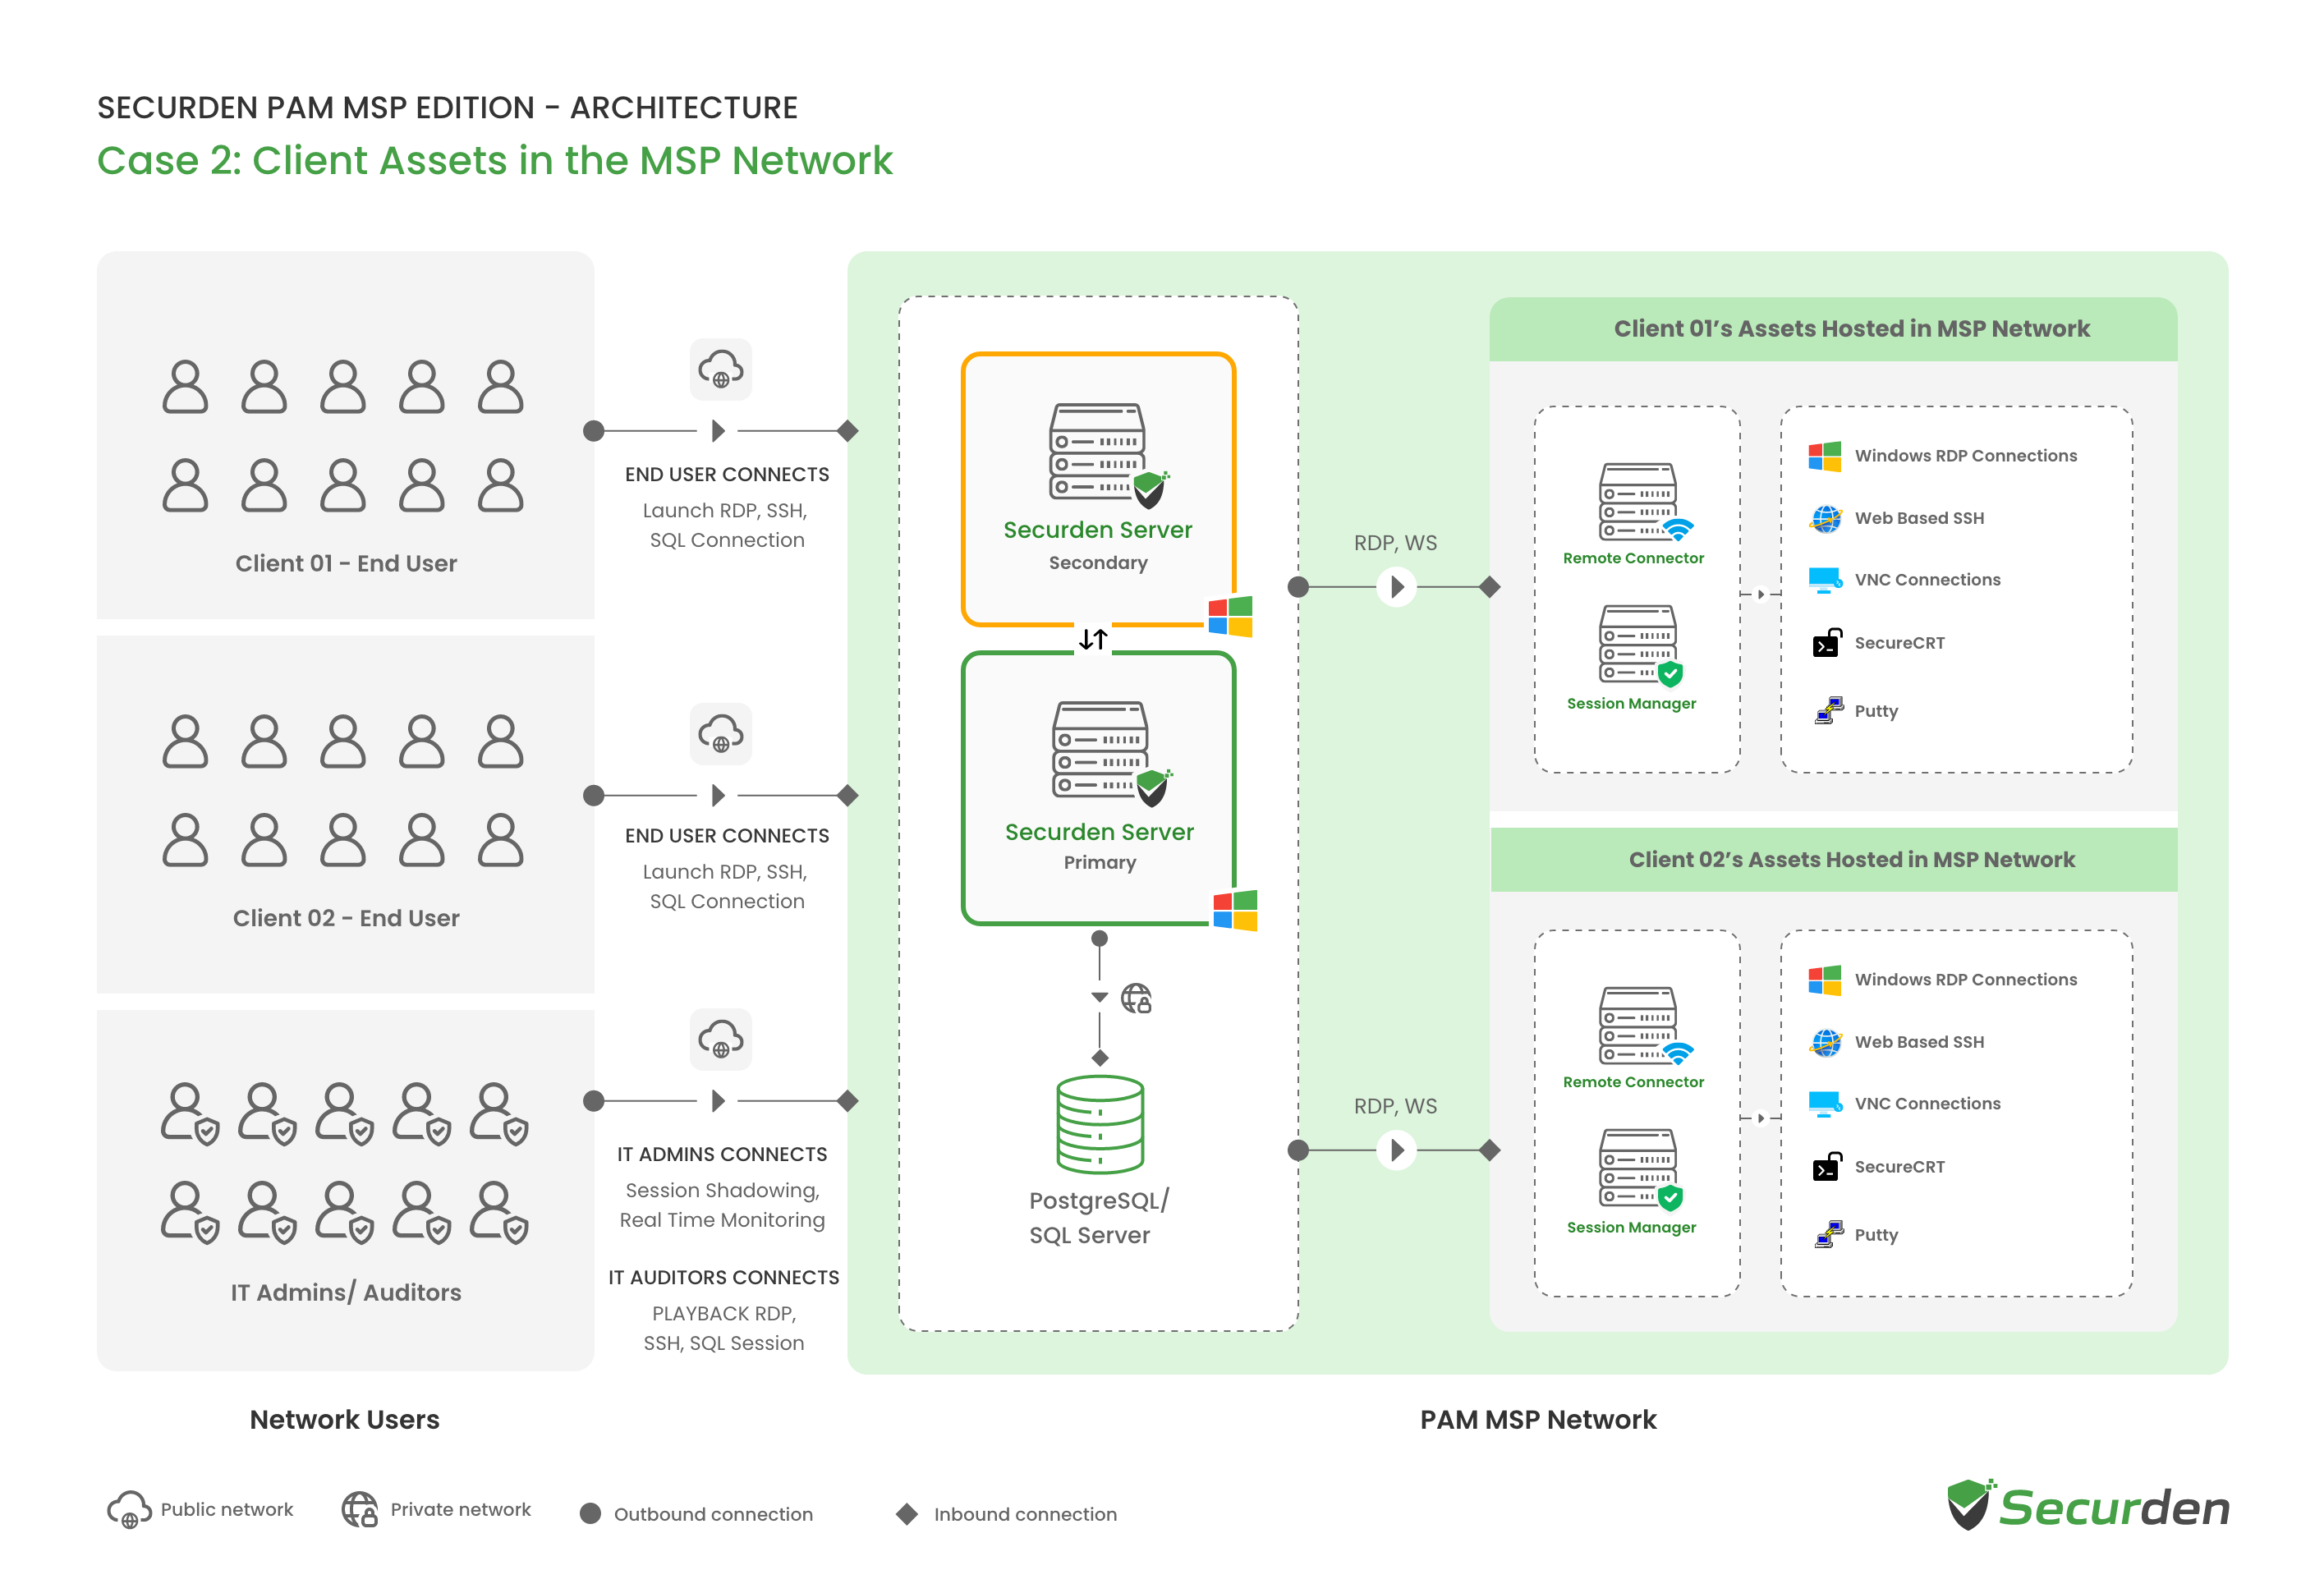
Case 2: Client Assets in the MSP Network
The privileged systems belonging to different client organizations reside within the MSP network. Connections between the PAM server and each client's privileged systems are routed through a Remote Connector. Communication between the Remote Connector and the PAM server takes place over Secure WebSocket.
Case 3: Client Assets Across Both Networks
The client's privileged systems are distributed across the MSP network and its own network. The PAM server communicates with privileged systems residing in client networks through Remote Connectors deployed within those networks (via outbound Secure WebSocket connections). The architecture also utilizes Remote Connectors to route connections to client assets located within the MSP network.
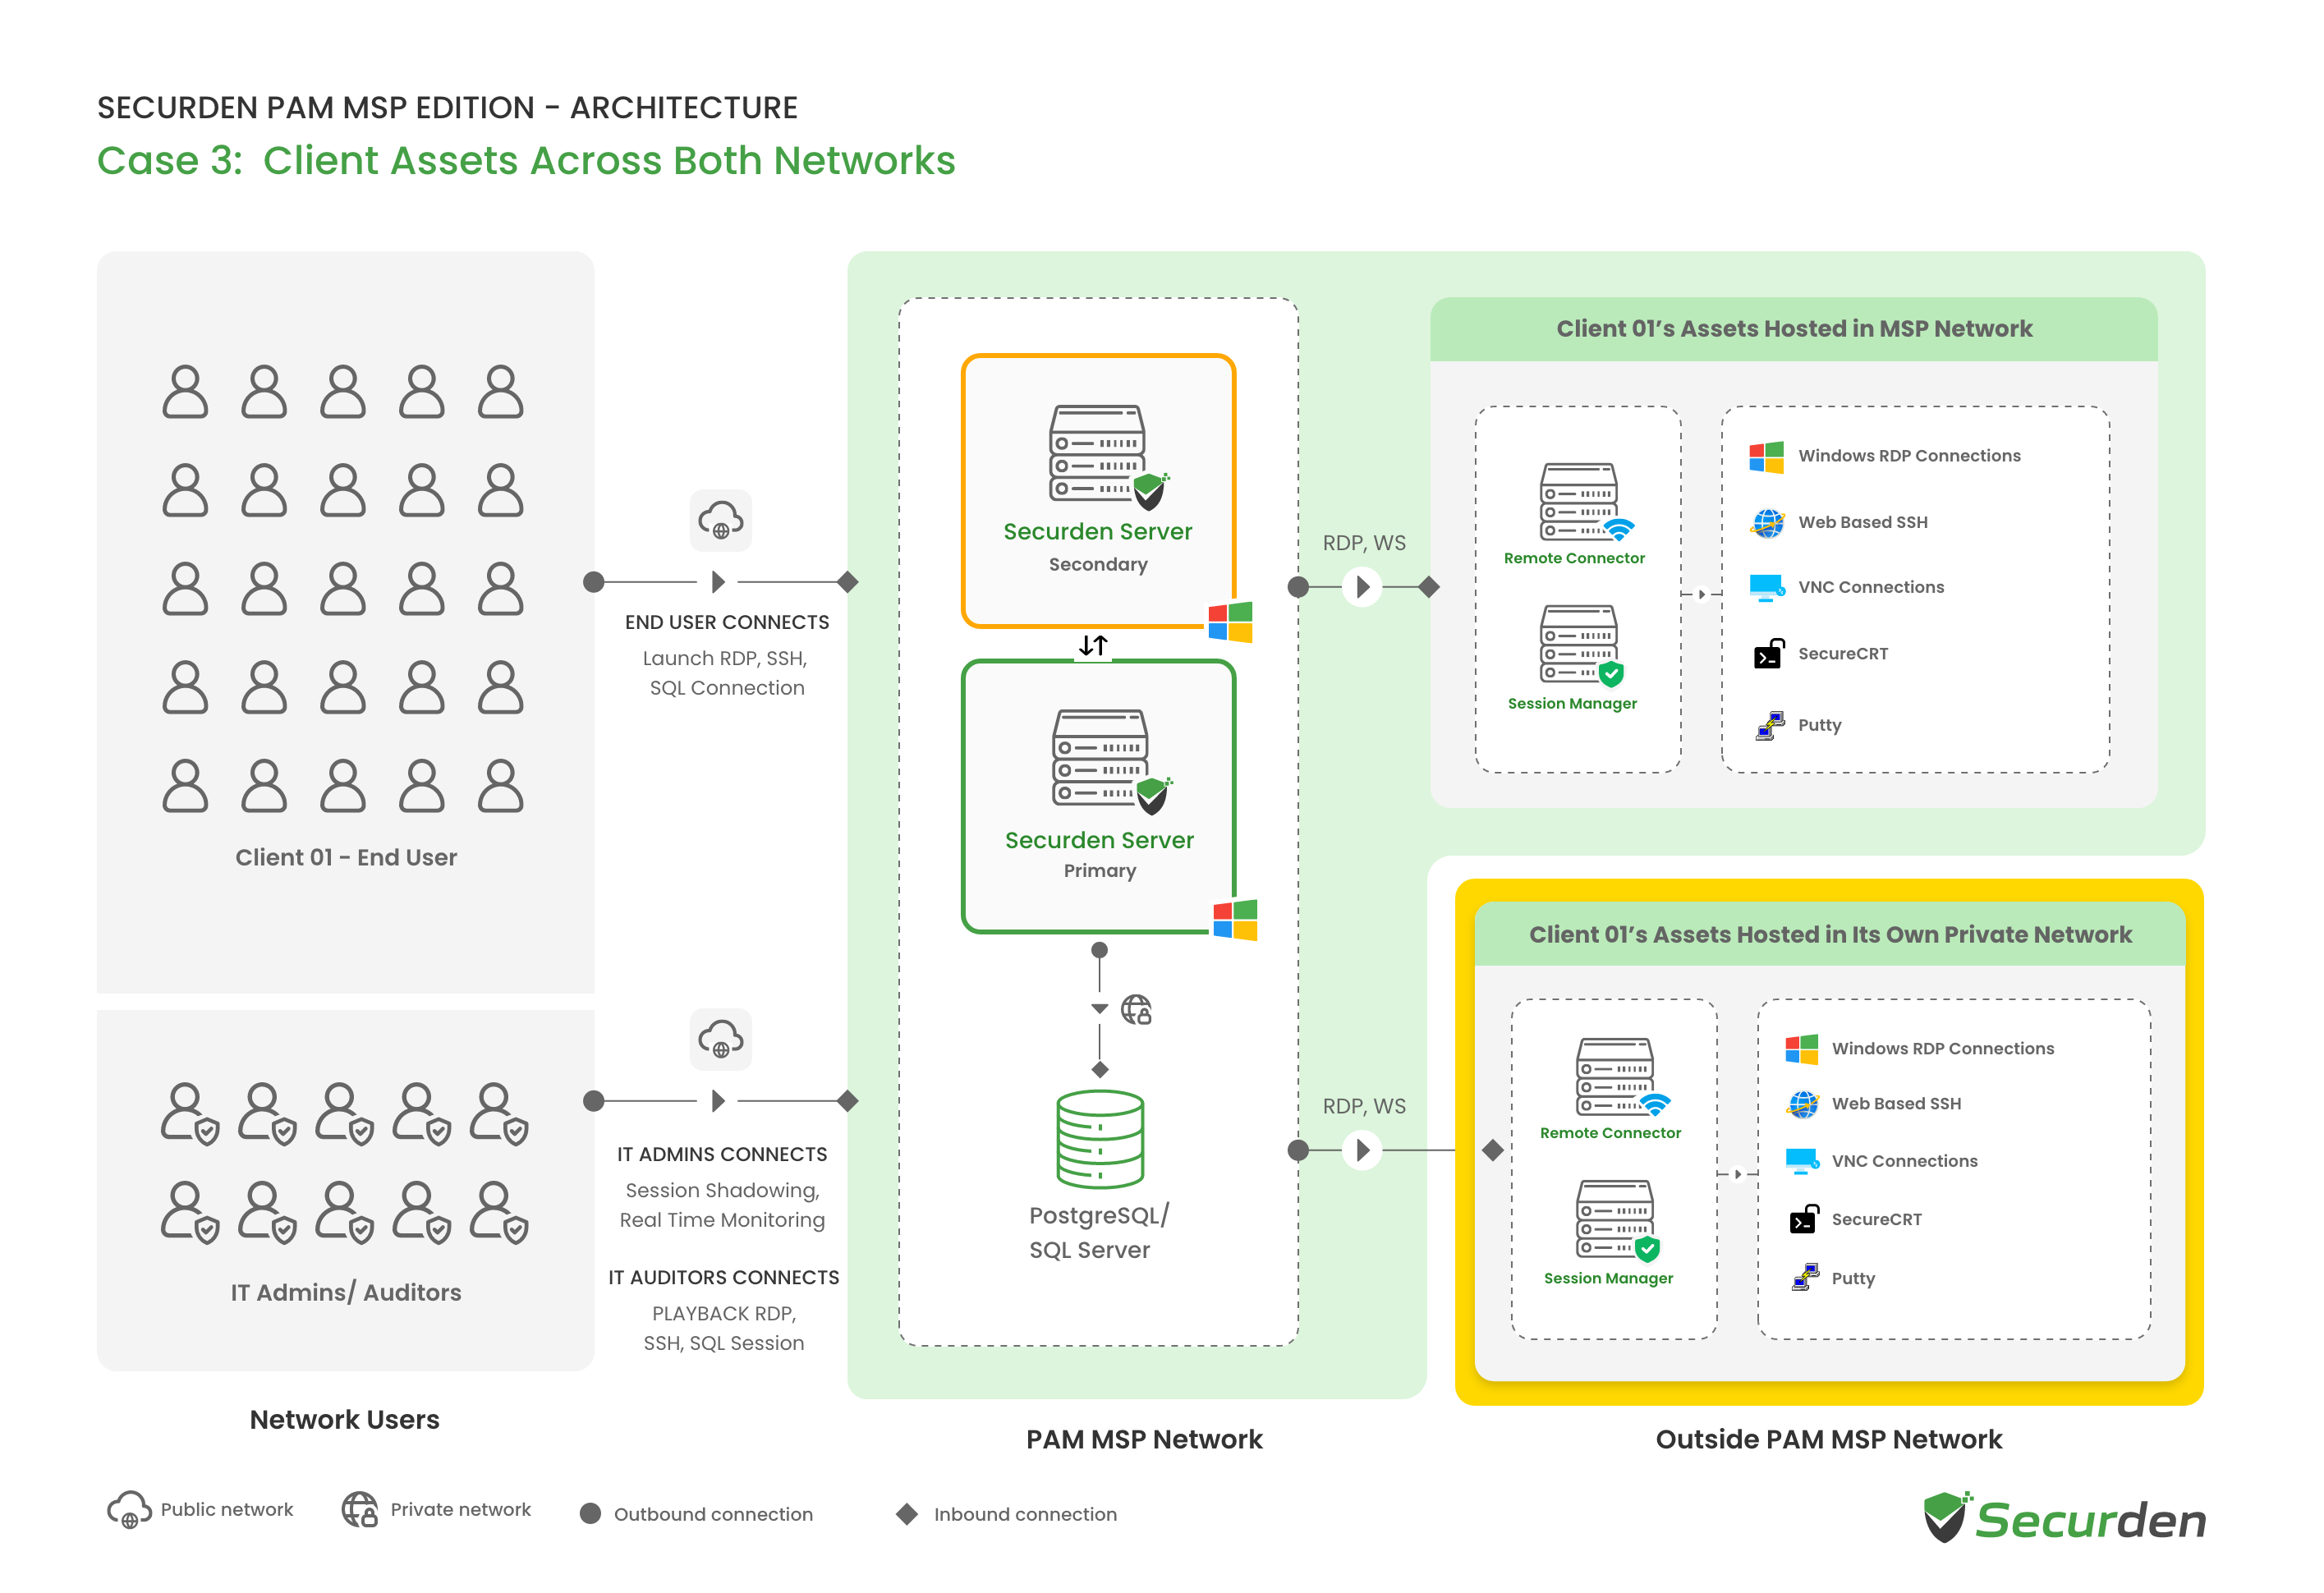
Note: Cases 1 and 2 can occur independently or in combination, depending on where each client’s assets reside. All three cases can be handled simultaneously by a single Securden PAM: MSP Edition instance.