- On-prem
- SaaS
PAM Architecture Overview
Securden Unified PAM is a web-based, on-premises, self-hosted solution delivered as a single, self-contained software package for installation on Windows servers. The package includes all essential components, including an embedded web server and a bundled PostgreSQL database, eliminating the need for additional software dependencies. Microsoft SQL Server is also supported as an alternative database backend.
The solution follows a centralized architecture, with the application server managing business logic, authentication, access controls, and administrative operations. End users access the platform through standard web browsers, without requiring agents or additional software installations on their endpoints.
Secure Remote Access and Session Management
Securden employs a gateway-based architecture using Securden Session Manager (SSM), deployed on a designated host within the enterprise network. SSM securely brokers RDP, SSH, and SQL connections to target systems while supporting privileged session management, monitoring, and recording.
By routing remote sessions through the SSM gateway, the architecture eliminates the need for direct connectivity between user endpoints and sensitive IT assets by default. This provides centralized control over privileged access and reduces the exposure of critical infrastructure.
High Availability and Distributed Deployment
Securden supports a high-availability architecture (active-active model) comprising a primary application server and a standby secondary server, each maintaining its own database. Both servers operate concurrently, with encrypted streaming replication from the primary database to the secondary database, enabling the standby server to assume operations in the event of a primary server failure.
For larger or geographically distributed environments, additional application servers can be deployed to distribute workloads and improve scalability without requiring separate database replication.
Read-only replica servers can also be deployed across distributed networks to facilitate password retrieval and remote connections, improving access efficiency and reducing dependence on a centralized deployment.
Vault Design, Encryption Standards, Key Management
Securden protects sensitive information through a fully encrypted vault using AES-256 encryption. Encryption is performed at the application layer before information is written to the database, ensuring that sensitive data remains protected at rest.
Each installation uses a uniquely generated encryption key. For enhanced security, the key can be stored separately from the application server, either in a protected network location accessed through a dedicated service account or within a connected Hardware Security Module (HSM).
All sensitive data at rest is protected using AES-256 encryption, while data transmitted during remote sessions and other remote operations is secured through TLS/SSL-encrypted communication channels.
Together, these architectural capabilities provide centralized privileged access control, secure remote connectivity, high availability, distributed scalability, and strong data protection, supporting deployment in complex enterprise environments.
Core Architectural Components
Unified PAM consolidates the various components for privileged operations, elevated admin rights, and protected access to your IT infrastructure. The core components of Unified PAM are explained below and illustrated in the architecture diagram.
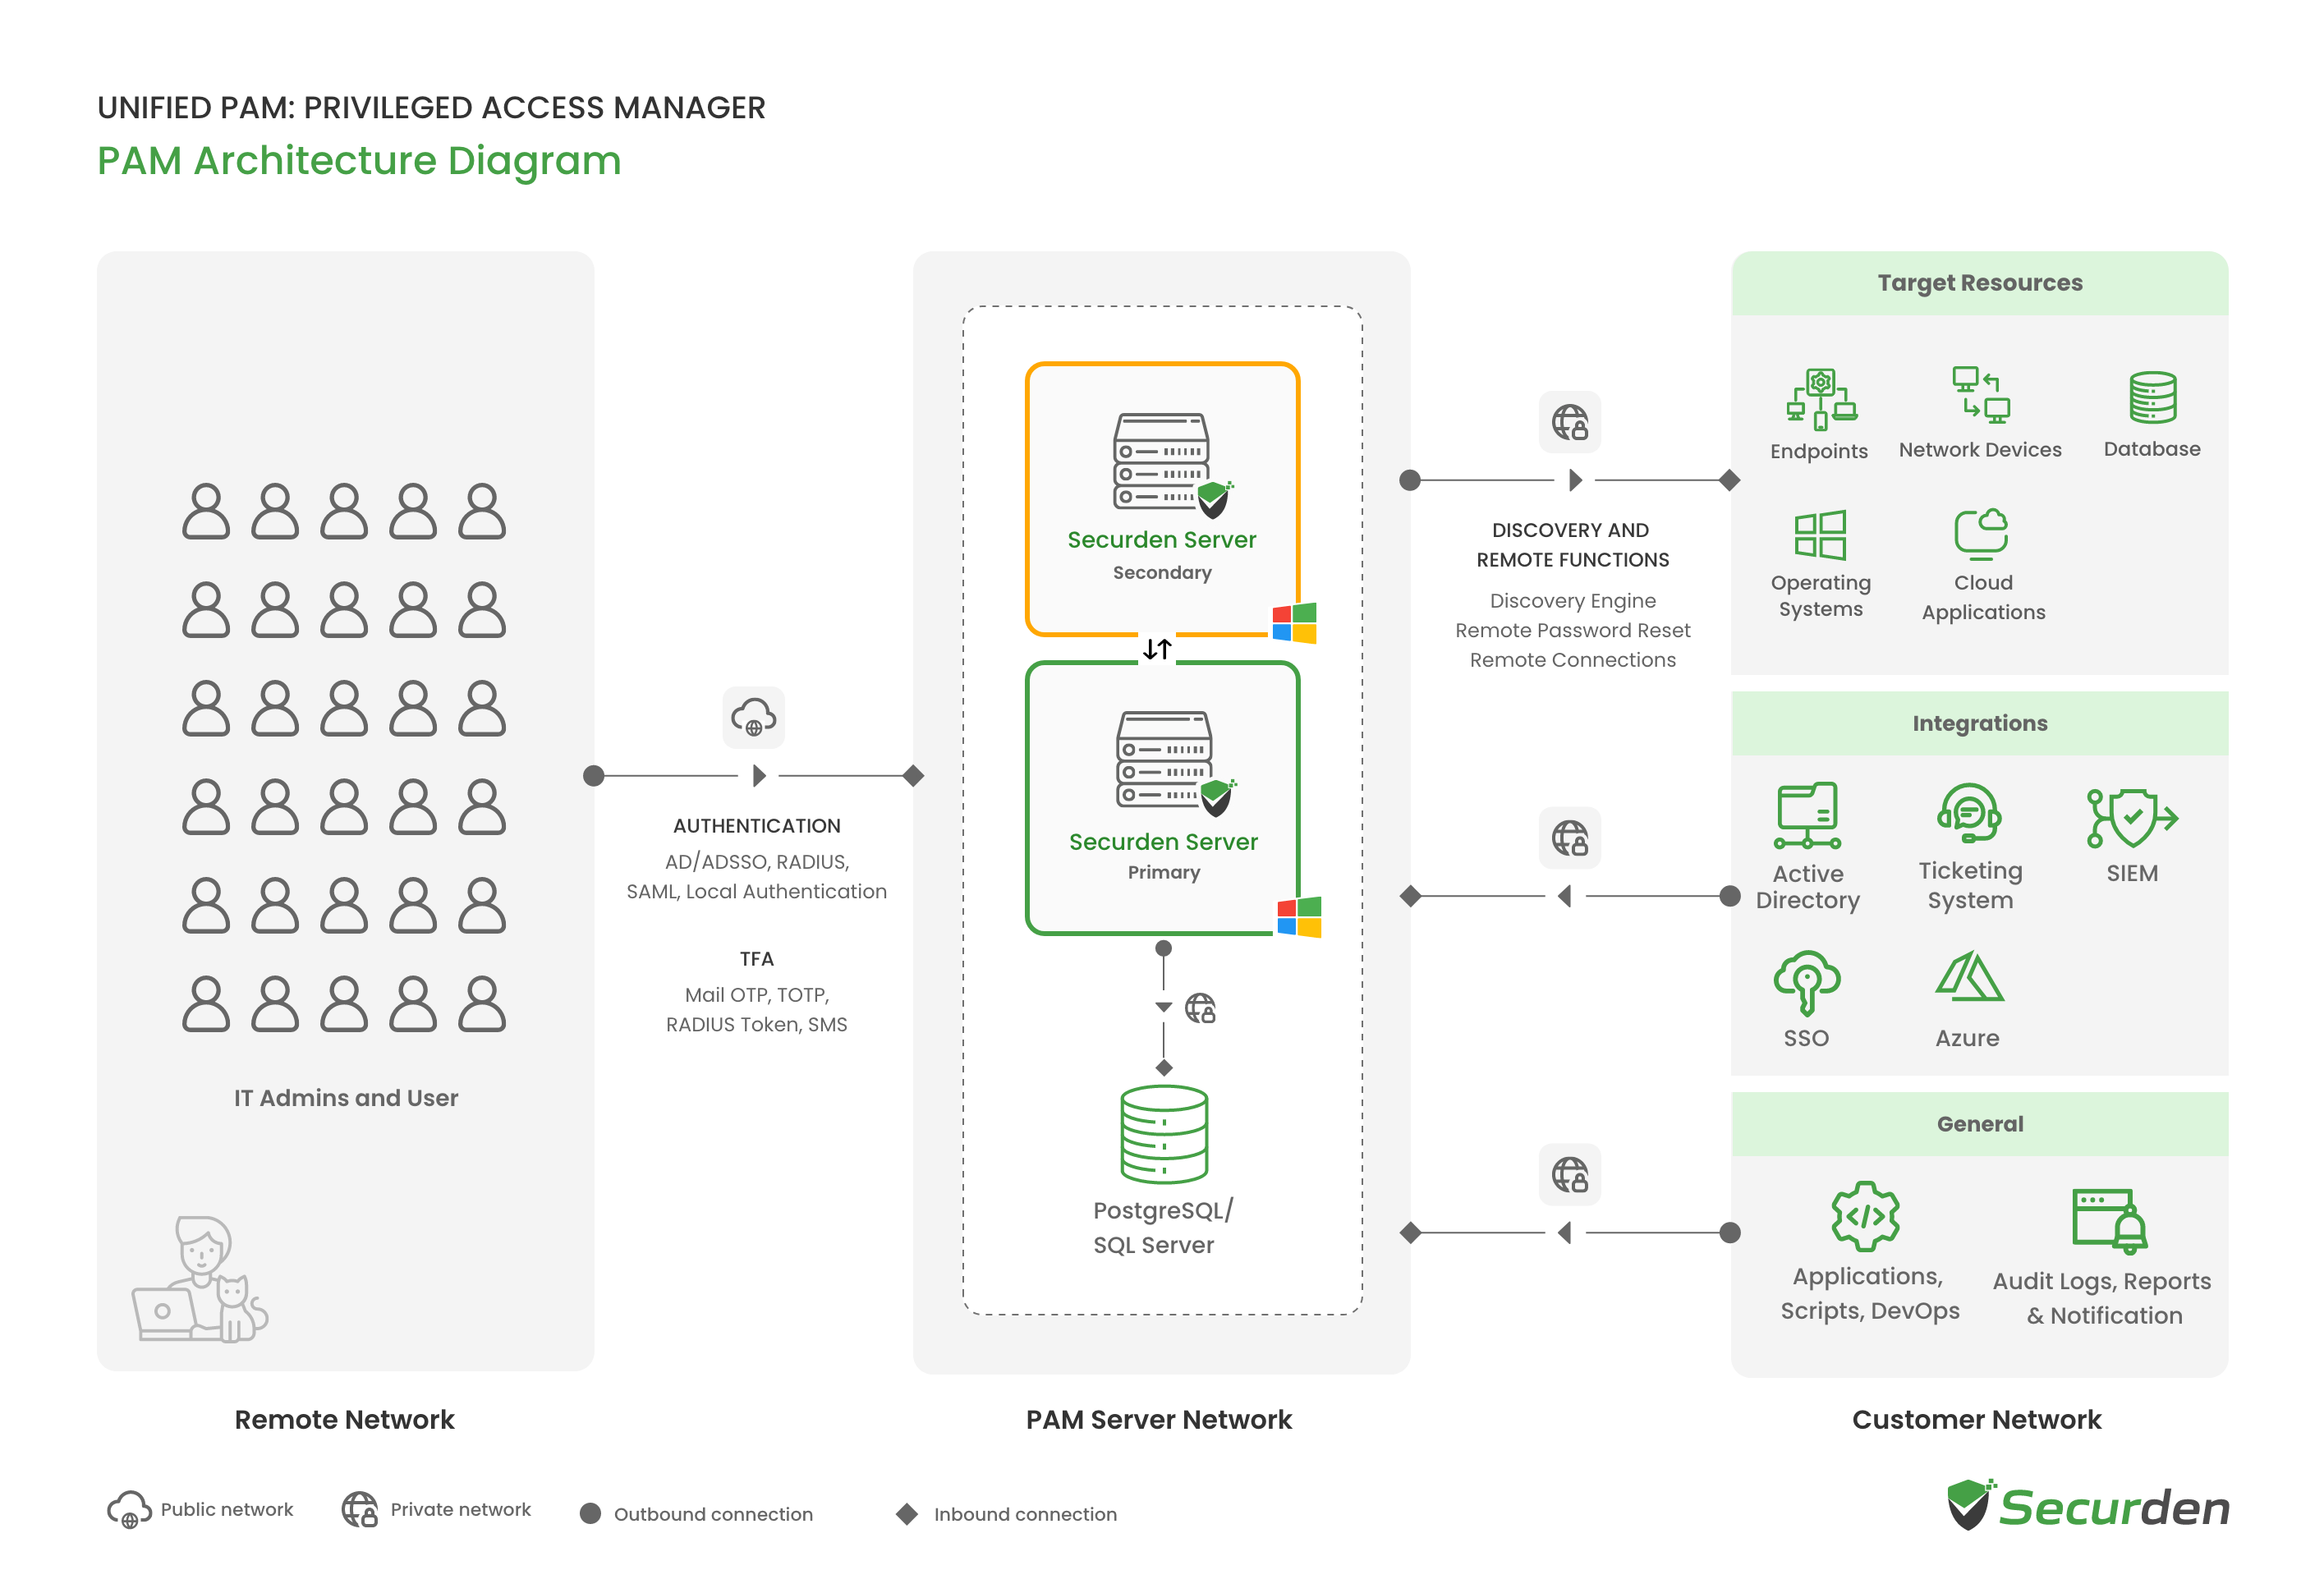
1) Application Interface
The Unified PAM interface is accessible by users through any standard web browser. Users are imported from any organizational directory such as AD, Entra ID, LDAP, or through files. They can login using their organization's designated Securden Server URL.
- Multifactor Authentication & SSO: In addition to the username & password or SSO for login – Securden integrates with a variety of MFA providers for added security before accessing PAM.
2) Primary Application Server
The Unified PAM Application is Deployed via ZIP package on a Windows machine (Virtual or Physical). It connects to the bundled PostgreSQL database to store all sensitive data in a highly-secure encrypted format.
The Password Vault forms the core of all PAM operations – leveraging the passwords, keys, service accounts and other credentials for authentication. While Unified PAM is vault-centric, access to various systems can be launched by using ephemeral (short-lived) credentials that do not rely on fetching login details from the vault.
3) Database
The bundled PostgreSQL database, or, optionally, a Microsoft SQL Server instance, holding all sensitive data in AES-256-encrypted form.
4) Secondary (Standby) Server(s)
Having one or more secondary application servers facilitates continuous uptime and provides a highly available setup to accommodate emergencies such as heavy traffic spikes, server outage, network issues, network latency, etc.
You can either map the secondary server to the database of the primary server or have a secondary (standby) database that will constantly replicate data from the primary server.
- Read-Only Server(s): The read-only server helps users access Securden when the primary server is down. The replica server, however, only allows users to perform ‘READ’ operations. This prevents them from modifying data. Based on your requirements, any number of Read-Only servers can be set up in various locations.
5) Application Servers/Remote Connectors (Optional, without database)
Remote connectors are additional servers that can be deployed for load distribution and to support distributed or multi-site networks from the central installation. The remote connector performs privileged account discovery, password verification, password rotation, directory synchronization, and policy enforcement across Vault, PAM, and EPM workflows in the remote network where it is deployed.
6) Remote Gateway: SSM Jump Server(s)
The SSM facilitates secure privileged session launch (RDP/SSH/SQL/HTTPS), monitoring, recording, and policy enforcement for administrative access to internal infrastructure in the network where it is deployed. This approach eliminates the need for direct connectivity between the endpoints and the sensitive IT infrastructure and ensures a higher level of security.
Each session manager can handle multiple simultaneous sessions and needs to be sized accordingly.
7) Encryption Key & Security
Unified PAM stores all sensitive information in a fully encrypted manner in a secure, digital vault. Securden uses AES-256 for encryption. The encryption key is unique to every installation and is automatically generated.
The best way to safeguard the key is to store it in a network location that is not on primary or secondary (in a separate machine) and use a dedicated service account to access the location for read or write operations. You can also use the same service account to run the Securden service so that only Securden has access to that location, and even if the servers where Securden is installed are compromised, the key isn't available on that server. You can alternatively store the key in a secure location, such as a mounted physical Hardware Security Module (HSM).
- Data in Transit: All remote sessions, administration traffic, and operational management tasks are encrypted using TLS/SSL over secure network channels.
High Availability & Scalability
- Active-Standby HA: High availability uses two application servers (primary and secondary) connected to a common database keep privileged credentials highly available. If one server fails or becomes unresponsive: incoming traffic is redirected to the other active server. The HA servers can be two separate physical machines or two virtual machines.
- Optionally, the Secondary (Standby) server can maintain its own database instance with encrypted streaming database replication from the primary for continuous failover readiness.
- Application Servers: Additional application servers (without local databases) can be deployed for load distribution across distributed or multi-site networks.
- Read-Only Replicas: Read-only replica servers can be deployed in remote segments to process local password retrieval and session launching while restricting data modification.
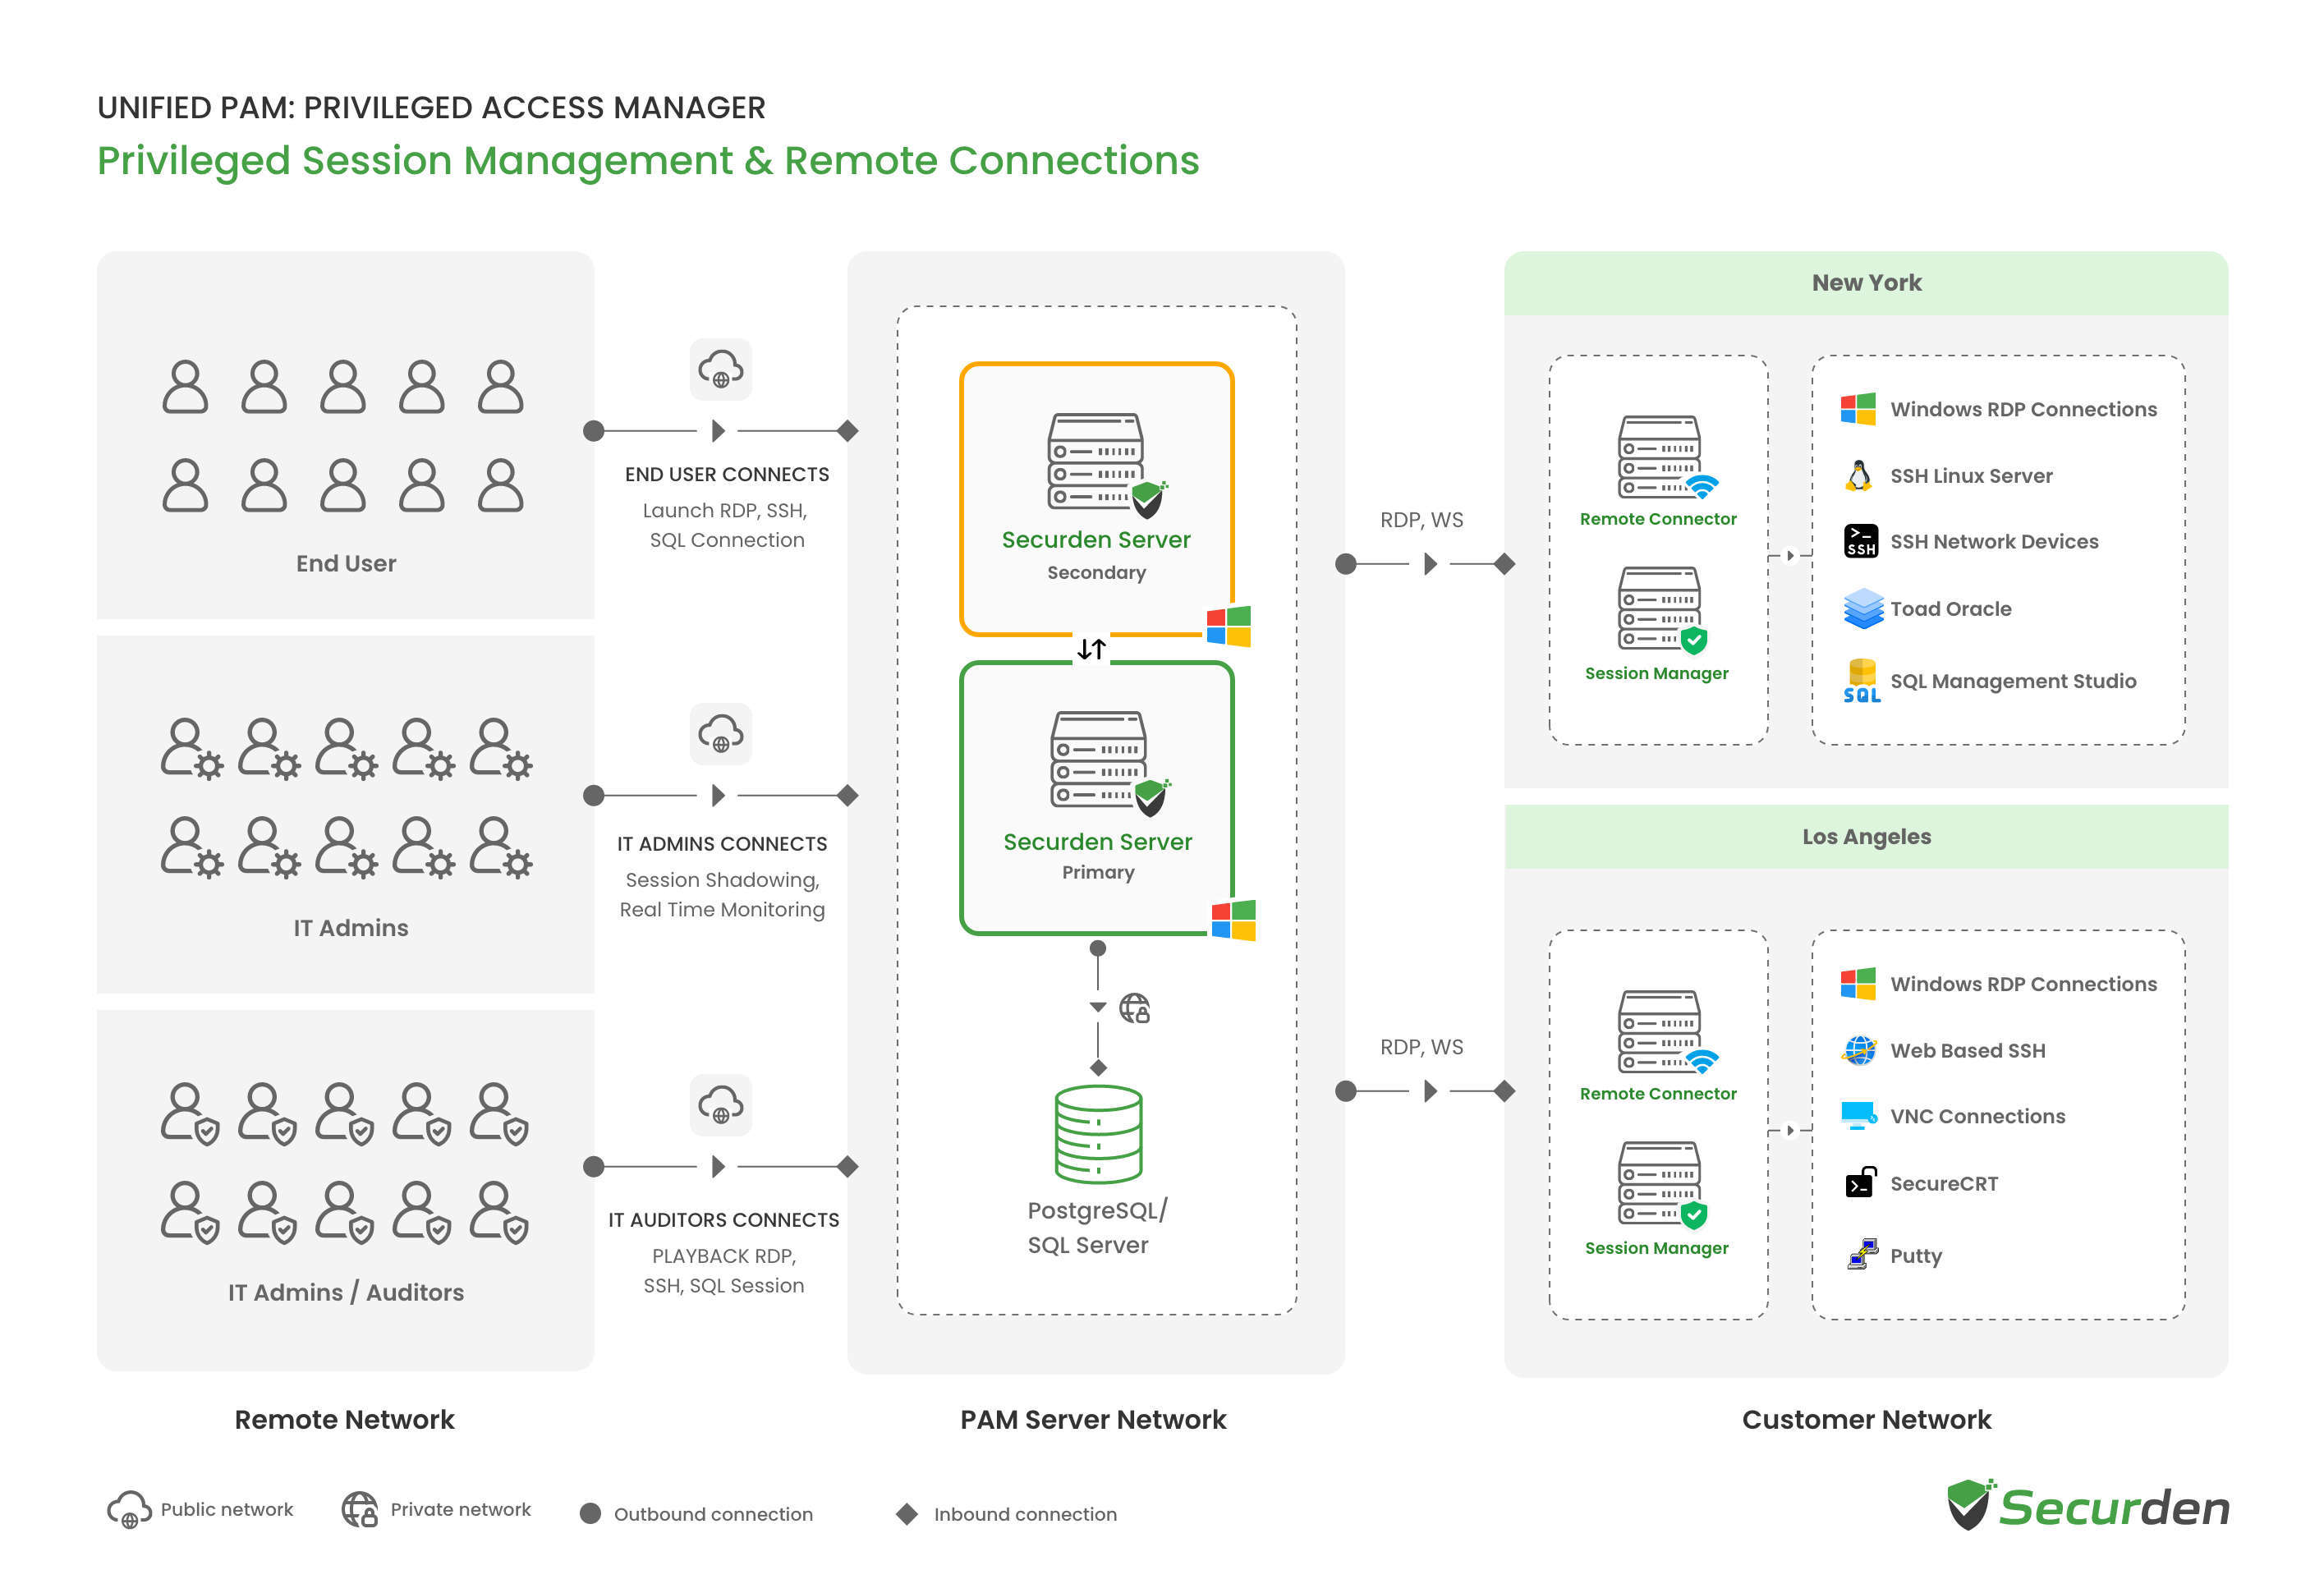
Data Flow
User access to the vault
- Users open the Securden web interface in a standard browser over HTTPS. No client software is required. Users can also access through desktop applications and mobile apps.
- The primary server (or an application server) processes the request and applies role-based access, approval workflows and MFA.
- Credentials are read from the backend database. They are stored AES-256 encrypted, and decryption happens at the application level on the server.
Remote privileged sessions
- A user launches a one-click RDP, SSH or SQL connection from the web interface.
- The request is routed to the Securden Session Manager on the jump host. All remote connections go through this gateway.
- The SSM brokers the connection to the target resource, so there is no direct connectivity between the user's machine and the sensitive asset by default.
- The session is monitored live and recorded. Audit trails and analytics are generated from it.
- Data in transit during remote sessions and remote operations is encrypted with TLS/SSL and sent only over secure channels.
Remote operations and discovery
- The Remote Operations Layer performs password resets, verification and account synchronization on target systems.
- Discovery connects to Windows hosts over WMI, and to Linux, Cisco and Mac devices over SSH. For databases, the relevant database ports are specified at scan time.
- Discovered accounts are imported into the vault and assigned ownership.
Replication and distribution
- The primary streams encrypted database replication to the secondary standby, which takes over if the primary fails.
- Application servers (no database of their own) connect to the central database to share load across sites.
- Read-only replicas serve password retrieval and remote connections locally in distributed networks.
Module Deployment Scenarios for Unified PAM
- The Password Management Module: The Password Vault module is activated to establish centralized privileged credential management. Users securely access the vault over HTTPS, while the Application Server integrates with AD/Entra ID for authentication and privileged account onboarding.
- The Core PAM Module (Privileged Accounts, Sessions, & Access): Once Vault foundations are established, Core PAM capabilities are enabled, including session routing through the SSM layer. Privileged access to VM, servers, databases, and network devices is governed through controlled workflows, with full monitoring, recording, and audit trails.
- The Vendor PAM Module (Third-Party, Contractor Access): Extending Core PAM for third parties, the Vendor PAM module governs vendor access without requiring persistent VPNs or internal network exposure. External users authenticate via an isolated cloud portal with strict multi-factor authentication (MFA), Just-In-Time (JIT) provisioning, and granular scope limits, while all external sessions remain fully isolated and recorded.
- The Endpoint Privilege Management (EPM) Module: The Endpoint Privilege Management module is activated to extend least-privilege enforcement across Windows, Mac, and Linux endpoints. EPM agents deployed across endpoints will periodically pull privilege elevation and application control policies from the Unified PAM server. This enables eliminating local administrator rights, granular application control, and establishing policy-based privilege elevation.
- The Cloud Infrastructure Entitlements (CIEM) Module: Building upon on-premises and hybrid access control, the CIEM module discovers, visualizes, and manages permissions across multi-cloud environments (AWS, Azure). It enforces least privilege by identifying over-permissioned identities (human and non-human), mitigating toxic combinations, and providing continuous risk modeling for cloud resources.
- The Remote Assistance Module: The Remote Assistance module extends PAM controls to end-user workstations and helpdesk workflows. Support teams can launch secure, attended or unattended remote support sessions to endpoints while still applying session recording, elevation-on-demand, and command control. This is done without granting permanent administrative rights to support staff or end users.
Module Configuration and Enablement
| Capabilities | Activities Performed |
|---|---|
| Password Vault | |
| Centralized encrypted credential storage, password randomization, ownership controls | Configure vault hierarchy, establish folder structures, enforce password complexity and rotation policies, define ownership and access controls, and enable credential expiration alerts. |
| Account Discovery | |
| Auto-discovery of privileged accounts across servers, databases, and network devices | Perform discovery scans, import discovered accounts into the vault, assign ownership, and onboard privileged identities target systems. |
| Session Management | |
| One-click remote privileged access (RDP/SSH/SQL/HTTPS), live monitoring, recording | Deploy and configure Securden Session Manager (SSM) instances to support high availability and load-balanced privileged session routing. Enable session recording, define retention policies, enforce session controls, and validate connectivity across infrastructure systems. |
| Remote Operations Layer | |
| Password resets, verification, account synchronization, privileged automation | To ensure resilience and continuous privileged operations. Configure connectors for account discovery, password rotation, verification workflows, and integration with Active Directory / Microsoft Entra ID. |
| Just-in-Time (JIT) Access | |
| Time-bound privilege elevation with approvals and auto-revocation | Configure approval hierarchies, justification requirements, time-bound access policies, and automatic privilege revocation workflows for sensitive administrative operations. |
| Privileged Session Analytics | |
| Session tracking, anomaly detection, usage monitoring | Enable session-level reporting, privileged activity insights, anomaly alerts, and administrator behaviour monitoring dashboards. |
| Endpoint Privileges & Vendor PAM | |
| Least privilege enforcement (EPM), isolated contractor access (Vendor PAM) | Deploy endpoint agents, configure Just-In-Time (JIT) access, set up vendor portals with MFA enforcement. |
| Integration Layer | |
| AD, SSO (SAML 2.0), MFA, SIEM, ITSM integrations | Establish and validate integrations with Active Directory / Microsoft Entra ID, configure SAML-based SSO, enforce MFA, and enable SIEM log forwarding and webhook-based event notifications. |
| Security Hardening | |
| Encryption, MFA enforcement, role-based governance, IP restrictions | Apply global security controls including enforced MFA, RBAC policies, IP-based access restrictions, administrative lock-down rules, and secure operational boundaries for privileged users. |
| Audit & Reporting | |
| Compliance reporting, event notifications, audit trails | Configure tamper-proof audit logging, scheduled compliance reports, privileged access dashboards, retention policies, and automated alerting mechanisms. |
Network and Port Requirements
All ports below are TCP unless otherwise noted. Submit and approve firewall changes across all target subnets before deployment, including client-to-gateway and gateway-to-target ports for remote protocols.
Primary Product Ports
| Port name | Source | Destination | Port |
|---|---|---|---|
| PostgreSQL database Default backend RDBMS connection |
Primary, Secondary and all Application Servers | PostgreSQL server | 5858 |
| MS SQL database Only if MS SQL Server is the backend |
Primary and Application Servers | MS SQL server | 1433 |
| Securden server (web) Web port; can be changed to 443 or another port |
All users (end machines), agents and Secondary servers | Primary server | 5959 |
| Securden server (web) Web port; can be changed to 443 or another port |
All users (end machines), agents and Secondary servers | Secondary server | 5959 |
| SSM inbound Opened on the SSM for all client machines |
All client machines | SSM server machine(s) | 3389 (RDP) |
| SSM outbound Opened to all target machines from the SSM server |
SSM server machine(s) | All target machines | 3389 (RDP) |
| Web SSH Web-based SSH remote connections |
All users (end machines) | All Application Servers | 5622 |
| Web RDP Web-based RDP remote connections |
All users (end machines) | All Application Servers | 5626 |
| Session recording (web applications) Required for web application session recording captured by the Browser Extension |
Browser Extension component | All Application Servers | 5936 |
| SMTP (TLS) Mail delivery using TLS |
Application server | Mail server | 587 |
| SMTP (SSL) Mail delivery using SSL |
Application server | Mail server | 465 |
Directory, Authentication and Integration Ports
| Port name | Source | Destination | Port |
|---|---|---|---|
| Proxy server Only if a proxy regulates internet traffic; configured under Admin > General > Proxy Server Settings |
Primary server | Proxy server | Based on your settings |
| AD (DC), secure SSL/TLS; used for Active Directory account discovery (default) |
Primary server | AD domain controller | 636 (TCP) |
| AD (DC), standard Used only if SSL/TLS is not enabled |
Primary server | AD domain controller | 389 (TCP) |
| RADIUS server Only if RADIUS-based two-factor authentication is configured |
PAM servers | RADIUS / MFA server | 1812 |
| Entra ID (Azure AD) Only if Entra ID integration is used |
Primary / Application server | Entra ID | Graph API (HTTPS) |
| Breached password identification Checks for breached or compromised passwords |
Primary server (needs internet access) | api.pwnedpasswords.com | HTTPS |
| Windows WMI Discovery Local Windows system/account discovery |
Application / Connectors | Windows Assets | 135 |
| SSH Device Discovery SSH discovery across network devices |
Application / Connectors | Linux, Cisco, Mac Assets | 22 |
| Database Discovery Ports specified at scan time (e.g., 1433, 1521, 3306, 5432) |
Application / Connectors | Target Database Host | DB Specific |
Note:
- The Securden web port (default 5959) may be changed to 443 or any other available port.
- The AD port defaults to 636; 389 applies only when SSL/TLS is not enabled for the directory connection.
Data Protection Summary
| State | Protection |
|---|---|
| At rest | AES-256, applied at the application level before storage |
| In transit | TLS/SSL over secure channels |
| Key management | Unique per-installation key, stored on a separate network location via a dedicated service account, or in an HSM |
Cloud PAM Architecture Overview
Securden Unified PAM (Privileged Access Manager) is a web-based, fully-hosted software solution that is delivered on AWS cloud. Securden partners with AWS data centers to provide Unified PAM as a Service to customers across various regions. AWS provides an RDS for PostgreSQL database which is redundant and highly available. The data centers are also HIPAA and PDPA compliant.
Infrastructure Operations: Fully Managed by Securden
The cloud edition of Unified PAM does not require provisioning application servers, databases, SSL certificates, or standby infrastructure. All backend services, automatic backups, patches and updates, encryption, and infrastructure uptime for high availability are managed by Securden within the SaaS platform.
How it Works
The solution runs on a central AWS server that handles all business logic, and end users connect through any standard web browser with nothing installed on their machines. Optionally, as per convenience they can make use of the Unified PAM desktop or mobile application.
Remote Connections
For remote connections, session management, and recordings, Securden uses a gateway model based on the Securden Session Manager (SSM), deployed on a jump host within the network to broker RDP, SSH, and SQL connections. All remote connections from endpoints to target resources are routed through this gateway, eliminating direct connectivity between end-user machines and sensitive IT assets by default.
Unified PAM can be deployed as a single solution that consolidates:
- Password Management (Vaulting)
- Privileged Access and Session Management (PASM)
- Privilege Elevation & Delegation Management (PEDM)
- Vendor Access Management (VPAM)
- Cloud Infrastructure Entitlements Management (CIEM)
- Secure Remote Access & Assistance (SRA)
- Non-human & AI Identity Management [NHIM]
Securden has proven SaaS deployments across various government, banking, manufacturing, and healthcare organizations across the globe.
Setting up Unified PAM is very easy and quick; If you wish to test it out, we’ll send you the download links to your email address here.
Core Architectural Components
Cloud Privileged Access Management (PAM) architecture is the structure that consolidates the various components used for privileged operations, elevated admin rights, and protected access to your IT infrastructure.
The core components of Unified PAM SaaS are explained below.
Application Interface
The Unified PAM interface is accessible by users through any standard web browser. Users are imported from any organizational directory such as AD, Entra ID, LDAP, or through files. They can login using their organization's designated Securden Server URL.
Multifactor Authentication & SSO
In addition to the username & password or SSO for login – Securden integrates with a variety of MFA providers for added security before accessing PAM.
It supports TOTP authenticators like Google & Microsoft authenticators, any RADIUS-based authentication mechanism (RSA SecurID, Digipass, etc.), Duo Security, Yubikey, Email to SMS gateway and OTP through email.
Securden also supports FIDO2 & Web Auth-based Passkeys for secure, passwordless login.
The Remote Gateway: Jump Server for Distributed Networks
For remote operations like launching SSH, SQL, RDP connections, session monitoring & recording, password change & verification - Securden provides the option for a gateway approach. All remote connections from endpoints to target IT resources are routed through the remote gateway.
This approach eliminates the need for direct connectivity between the endpoints and the sensitive IT infrastructure and ensures a higher level of security.
Typically, you would install one remote gateway in each distributed network. The remote gateway consists of two components. You can deploy one or both depending on your requirements.
Gateway Component 1: The Remote Connector
The Remote Connector is Deployed via ZIP package on a Windows machine in your network.
The Remote Connector is required if you wish to
- Connect to on-prem AD for domain management or are using Active Directory Domain server in a private network that is not directly connected to cloud. To manage AD users using Securden, you should deploy Securden Remote Connector in your network.
- Add and manage accounts from servers (AD), databases (SQL/POSTGRESQL/Oracle/MySQL) or network devices (Cisco IOS).
- Carry out remote operations such as password reset, launching connections to IT assets etc.
Note: For distributed networks, you would need to deploy the Securden Remote Connector in each of the networks where your users/servers/databases/devices reside.
Gateway Component 2: Securden Session Manager - SSM Server(s)
The SSM facilitates secure privileged session launch (RDP/SSH/SQL/HTTPS), monitoring, recording, and policy enforcement for administrative access to internal infrastructure in the network where it is deployed.
Each session manager can handle multiple simultaneous sessions and needs to be sized accordingly.
deployed on a jump host to broker and record Native RDP, SSH, and SQL sessions, ensuring no direct connectivity between end-user machines and target assets.
Encryption Key & Security
For every SaaS instance, the encryption is unique to each customer, and the encryption keys are managed using Amazon KMS along with AWS HSM for cryptographic operations.
Data in transit during remote sessions and remote operations is encrypted using TLS/SSL and transmitted strictly over secure channels.
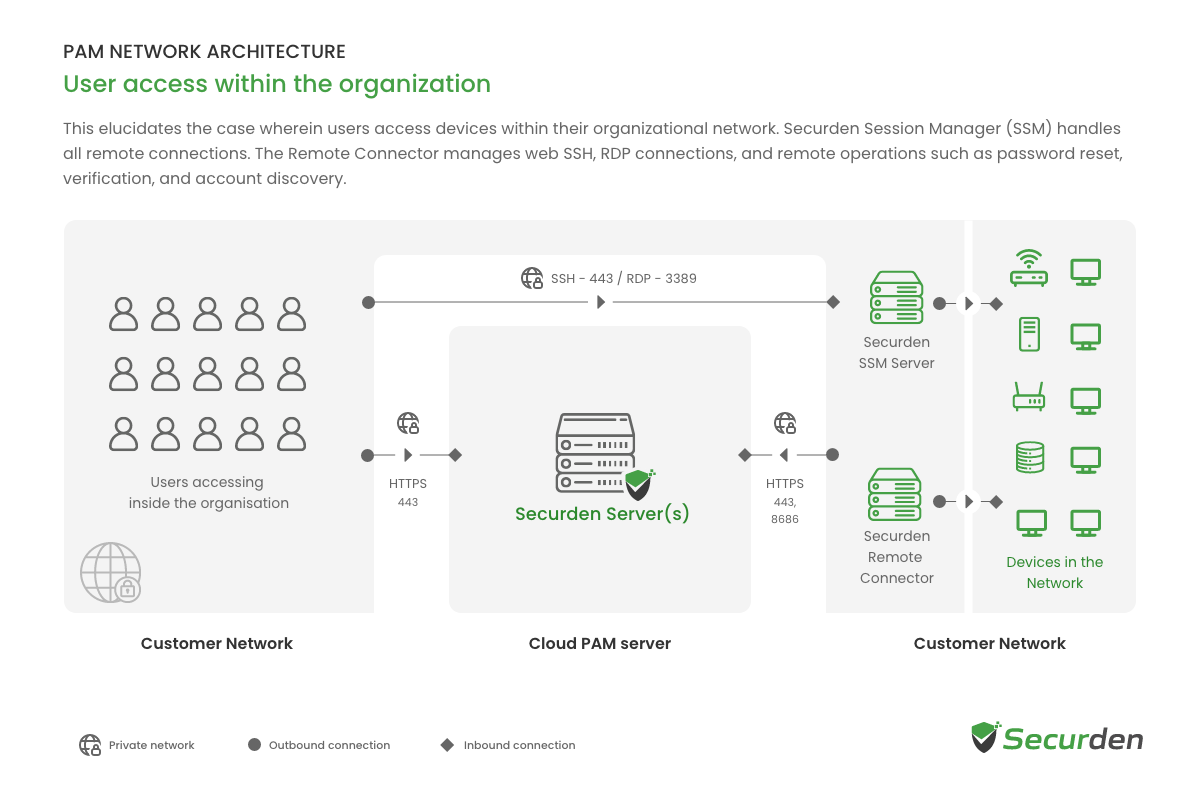
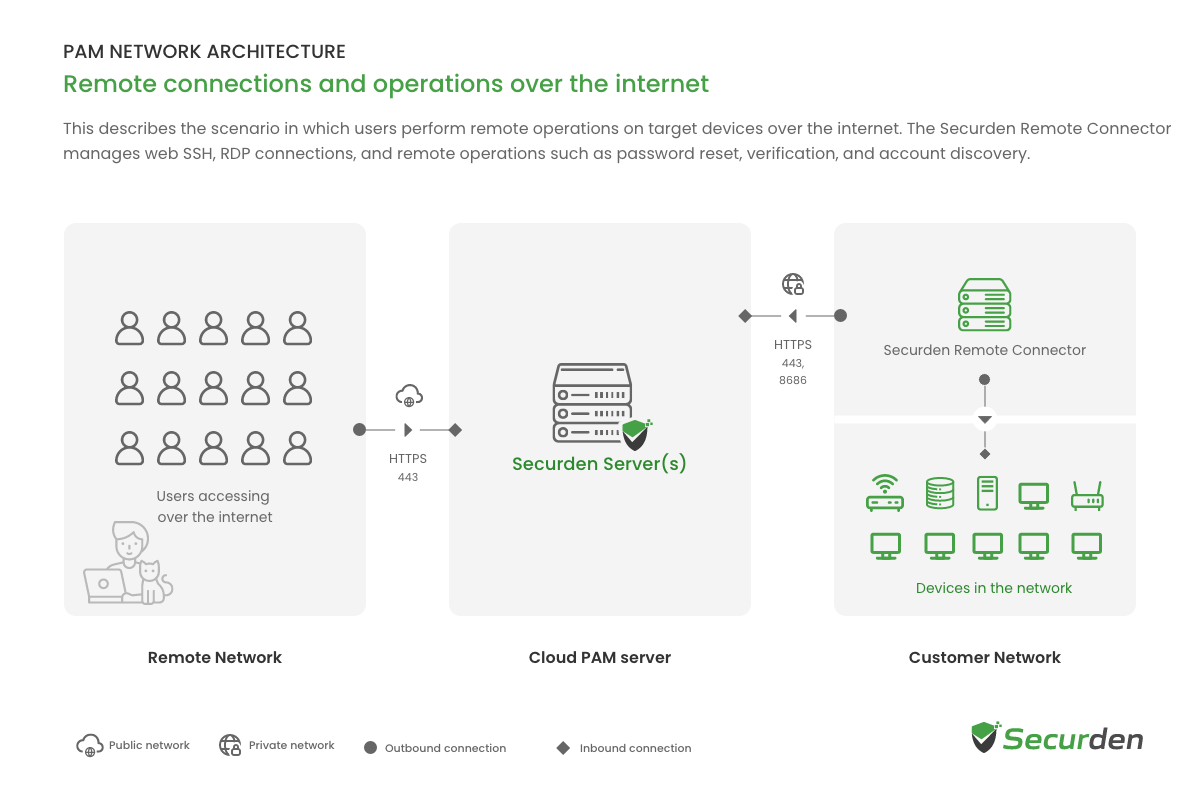
Cloud PAM Architecture Diagrams
Module Deployment Scenarios for Unified PAM
The Password Management Module
The Password Vault module is activated to establish centralized privileged credential management. Users securely access the vault over HTTPS, while the Application Server integrates with AD/Entra ID for authentication and privileged account onboarding.
The Core PAM Module (Privileged Accounts, Sessions, & Access)
Once Vault foundations are established, Core PAM capabilities are enabled, including session routing through the SSM layer. Privileged access to VM, servers, databases, and network devices is governed through controlled workflows, with full monitoring, recording, and audit trails.
The Vendor PAM Module (Third-Party, Contractor Access)
Extending Core PAM for third parties, the Vendor PAM module governs vendor access without requiring persistent VPNs or internal network exposure.
External users authenticate via an isolated cloud portal with strict multi-factor authentication (MFA), Just-In-Time (JIT) provisioning, and granular scope limits, while all external sessions remain fully isolated and recorded.
The Endpoint Privilege Management (EPM) Module
The Endpoint Privilege Management module is activated to extend least-privilege enforcement across Windows, Mac, and Linux endpoints. EPM agents deployed across endpoints will periodically pull privilege elevation and application control policies from the Unified PAM server. This enables eliminating local administrator rights, granular application control, and establishing policy-based privilege elevation.
The Cloud Infrastructure Entitlements (CIEM) Module
Building upon on-premises and hybrid access control, the CIEM module discovers, visualizes, and manages permissions across multi-cloud environments (AWS, Azure). It enforces least privilege by identifying over-permissioned identities (human and non-human), mitigating toxic combinations, and providing continuous risk modeling for cloud resources.